


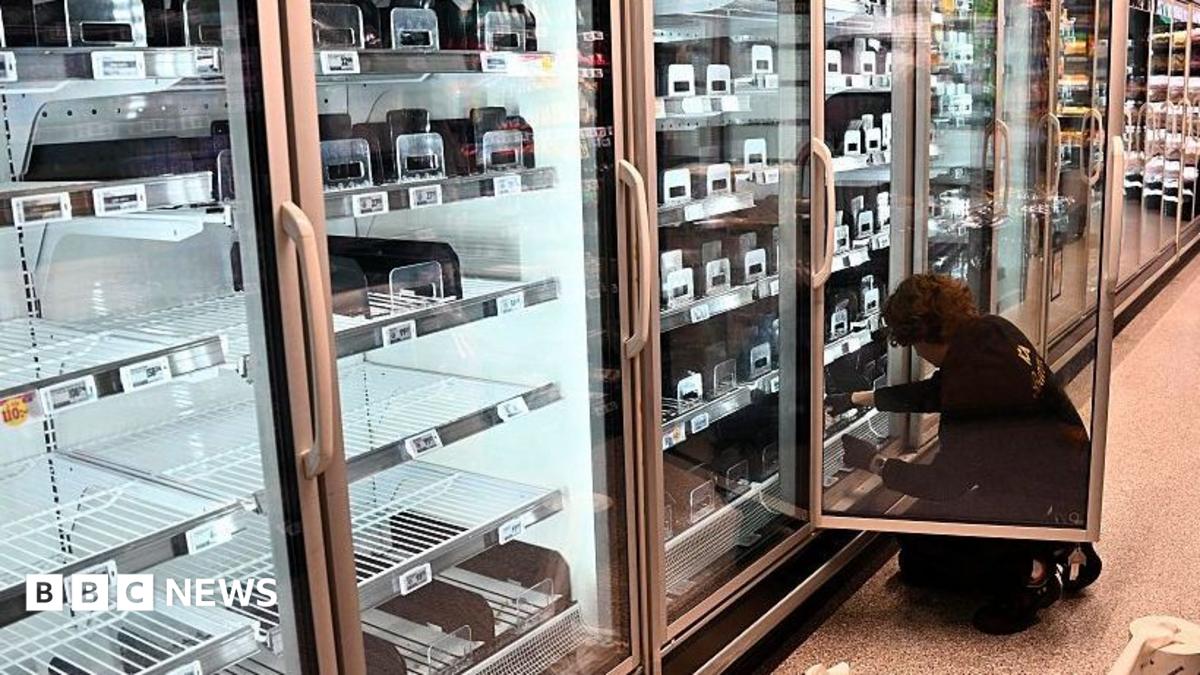
Two Russian hacktivist groups have claimed responsibility for a coordinated wave of cyberattacks on freezer systems at European supermarkets, but cybersecurity researchers remain uncertain about who was behind the incidents. Honeypot evidence suggests the second wave was highly targeted and planned, while possible perpetrators include Russian or Iranian hacktivists, state-backed hackers and teenagers carrying out pranks.
Russian groups claim responsibility
Noname057(16) and the Z-Pentest Alliance said on Telegram that they had collaborated on the attacks, claiming they had “proved once again their high level of skill and precision.”
However, the groups’ posts and channels have since been deleted, and their claims have been met with skepticism. Researchers have not ruled out a Russian group, but they say there is not yet enough evidence to confirm who carried out the attacks.
Honeypots track freezer attacks
Cybersecurity researchers from several companies are collecting evidence from “honeypots” to investigate the freezer hacks. Three cybersecurity firms have deployed fake freezer software traps designed to monitor how attackers plan and conduct attacks.
In cybersecurity, a honeypot is a digital decoy, such as a fake computer network or file, deliberately made to appear vulnerable. It is intended to lure hackers, allowing security professionals to study their methods without exposing a genuine system.
Activity recorded after the first wave of attacks indicates that the second wave, which affected several European countries, was highly targeted.
Evidence of planning and coordination
“The fact that all these refrigerators and freezers were attacked at the same time suggests planning and coordination,” said Ryan Dewhurst of Spanish cybersecurity firm Previdian.
The affected freezer software products had entry points that were not difficult to exploit. Known attack vectors were already available online, while the systems were poorly protected.
Even so, experts such as Dewhurst said the attackers would have needed to identify the devices’ public IP addresses, build a target list and decide which techniques to use and when.
“Given the timing of the reported equipment temperatures, it appears that the greatest damage occurred overnight. This is further evidence that the attack was planned and coordinated,” he said.
Honeypots found activity focused on Europe
Strathclyde-based cybersecurity company Lupovis has also deployed honeypots to attract attackers and reveal their tactics. Honeypots are believed to be operating around the world, and activity targeting them began 10 days before the second wave of cyberattacks.
Lupovis said the hackers scanned and investigated fake freezer sites only in Europe.
“Our honeypots have never been targeted in places like Africa or South America,” said Lupovis founder Dr. Xavier Bereken.
“Vases were also left abandoned in Ukraine.”
Source: www.bbc.co.uk