


GitLab Patches Maximum-Severity RCE Flaw in Regular Expression Compiler
GitLab security teams should update vulnerable Community Edition and Enterprise Edition instances immediately. The company has released patches for a maximum-severity integer overflow vulnerability that could allow unauthenticated remote attackers to execute arbitrary code on affected GitLab servers under certain conditions.
GitLab CVE-2026-110264 enables potential remote code execution
The vulnerability is tracked as CVE-2026-110264. Security researcher joashkar reported the issue through GitLab’s HackerOne bug bounty program.
CVE-2026-110264 is an integer overflow weakness affecting GitLab’s regular expression compiler, a background engine that parses and validates regular expressions in configuration files.
GitLab says that an attacker could exploit the flaw by submitting a specially crafted regular expression. Under certain conditions, an unauthenticated user could then execute arbitrary code on a vulnerable GitLab server.
“GitLab has fixed an issue where an integer overflow when compiling a specially crafted regular expression could potentially allow unauthenticated users to execute arbitrary code on GitLab servers under certain conditions.”
GitLab versions fixed in the security update
GitLab fixed CVE-2026-110264 in the following Community Edition (CE) and Enterprise Edition (EE) versions:
- GitLab 19.5.1
- GitLab 19.4.3
- GitLab 19.3.6
- GitLab 19.2.9
- GitLab 19.1.9
- GitLab 19.0.10
- GitLab 18.11.13
GitLab strongly recommends that all installations running affected versions upgrade to the latest release as soon as possible.
“GitLab.com is already running a patched version,” the company said. “GitLab-only tenants running 19.3.5-internal0 and 19.4.2-internal0 or later already include these fixes and do not require any action.”
More than 2,700 GitLab CE instances exposed online
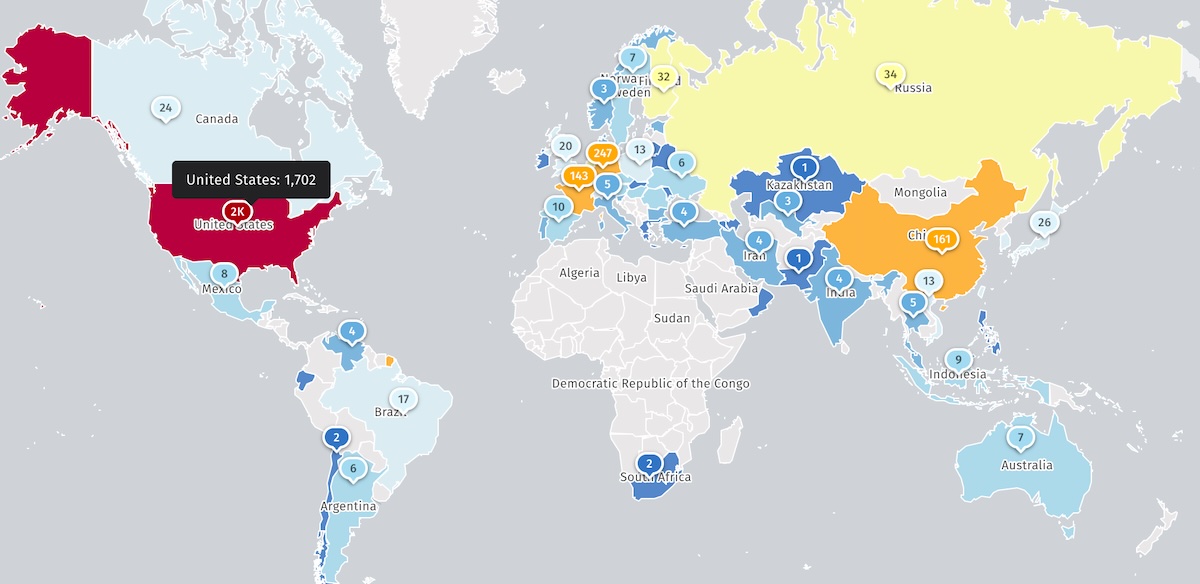
Internet threat watchdog Shadowserver is tracking more than 2,700 GitLab Community Edition instances accessible online.
However, Shadowserver does not provide information about how many of those systems are honeypots or have already been protected against attacks.
GitLab discloses multiple maximum-severity vulnerabilities
The latest issue follows another critical remote code execution vulnerability, CVE-2026-97229, which GitLab disclosed ten days ago. That flaw also affected the CI/CD regular expression compiler, had a CVSS base score of 10 out of 10, and was reported by the same security researchers.
Last month, GitLab fixed another maximum-severity CE/EE vulnerability, CVE-2026-85706. The flaw allowed unauthenticated attackers to read sensitive information, including credentials, from vulnerable servers.
The following day, the U.S. Cybersecurity and Infrastructure Security Agency (CISA) added CVE-2026-85706 to its Known Exploited Vulnerabilities catalog and ordered federal agencies to secure their systems within three days.
Since November 2021, CISA has flagged five GitLab vulnerabilities as exploited in the wild, including flaws used in ransomware attacks.
GitLab is widely used by large organizations
GitLab’s DevSecOps platform has more than 30 million registered users worldwide and is used by more than 50% of Fortune 100 companies, including Nvidia, T-Mobile, Lockheed Martin, Airbus, and Goldman Sachs.

The overall prevention score can hide what happens after the initial access. If an attacker uses valid credentials, your defenses drop sharply.
The Blue Report 2026 measures defense techniques by technology across 338 million simulations run in customer production environments.
Source: www.bleepingcomputer.com