


Attackers are scanning the Internet for unpatched Oracle E-Business Suite (EBS) systems affected by a recently disclosed critical vulnerability. Oracle released a security update for the flaw on October 20 and urged customers to apply the patch immediately, while threat intelligence company Defused has reported an exploratory exploit against a decoy EBS system.
Attackers scan for critical Oracle EBS vulnerability
Tracked as CVE-2026-101767, the vulnerability affects core components of the EBS Application Object Library. An unauthenticated attacker with HTTP network access can exploit the flaw through a low-complexity attack to take over a vulnerable system.
Oracle addressed the issue in its October 2026 Critical Patch Update, announced on October 20. The company urged customers to install the available security updates without delay.
“In some cases, attacks have been reported to be successful because targeted customers did not apply available Oracle patches,” Oracle said. “Therefore, Oracle strongly recommends that customers continue to use actively supported versions and apply security patches without delay.”
Oracle has not yet classified CVE-2026-101767 as actively exploited. However, threat intelligence firm Defused said Tuesday that it had already observed threat actors searching the Internet for vulnerable systems.
“Our Oracle E-Business Suite decoy recorded an exploratory exploit this morning, October 27, for CVE-2026-101767, an unauthenticated SQL injection into EBS’s Thin Client Framework servlet that chained to remote code execution,” Defused reported on X.
More than 670 EBS instances exposed online
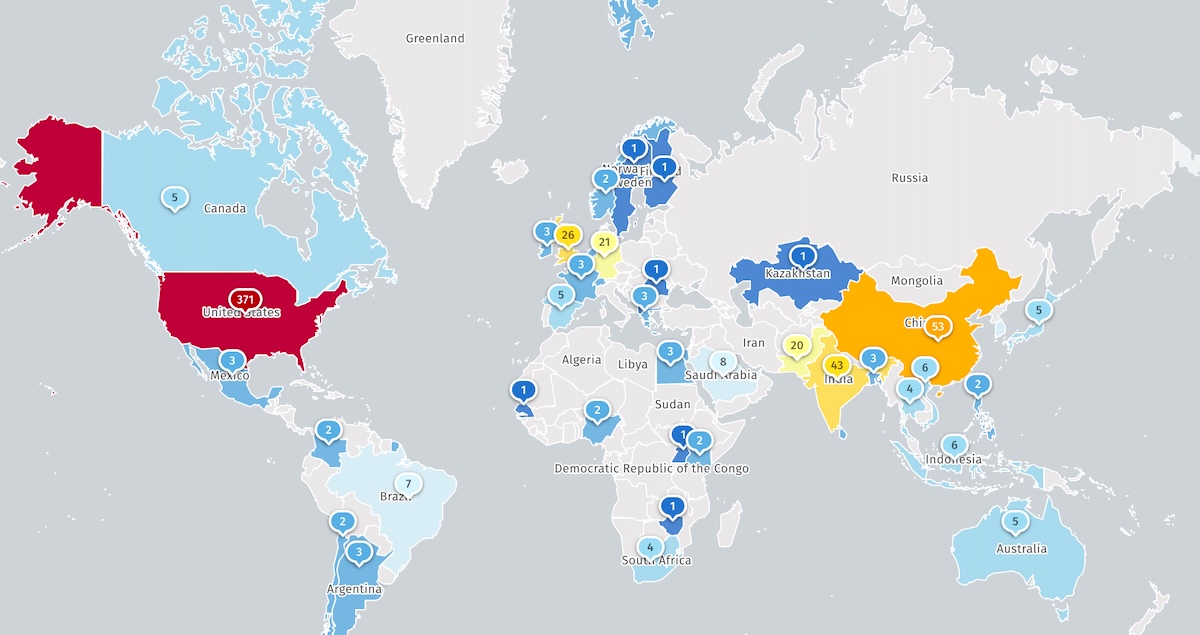
Internet threat monitoring organization Shadowserver tracks more than 670 Oracle EBS instances exposed to the Internet. Most of the identified systems have U.S. IP addresses.
Shadowserver does not indicate how many of the systems are honeypots or how many may already be protected against CVE-2026-101767.
Oracle vulnerabilities are frequently targeted because successful attacks can provide access to enterprise systems used by Fortune 100 companies, government agencies and healthcare organizations around the world.
Recent attacks targeted Oracle enterprise software
Since early August 2025, the Clop extortion gang has exploited another Oracle EBS vulnerability, CVE-2025-61882, in zero-day attacks. Reported victims included Logitech, GlobalLogic and The Washington Post, as well as U.S. universities such as Harvard University, the University of Pennsylvania, Dartmouth College and the University of Phoenix.
More recently, in June, Oracle released an emergency mitigation for a critical PeopleSoft Suite zero-day, CVE-2026-35273, which was exploited by the ShinyHunters extortion group from May 27 to June 9.
Attackers exploited that vulnerability to execute unauthenticated remote code on victims’ systems and steal data from organizations around the world, including the University of Nottingham, Nissan Motor Co., Ltd. and the National Association of Insurance Commissioners (NAIC).
Since November 2021, CISA has added 46 Oracle security bugs to its Known Exploited Vulnerabilities catalog. Thirteen of those vulnerabilities have also been used in ransomware attacks.

The overall prevention score can hide what happens after the initial access. If an attacker uses valid credentials, your defenses drop sharply.
The Blue Report 2026 measures defense techniques by technology across 338 million simulations run in customer production environments.
Source: www.bleepingcomputer.com