


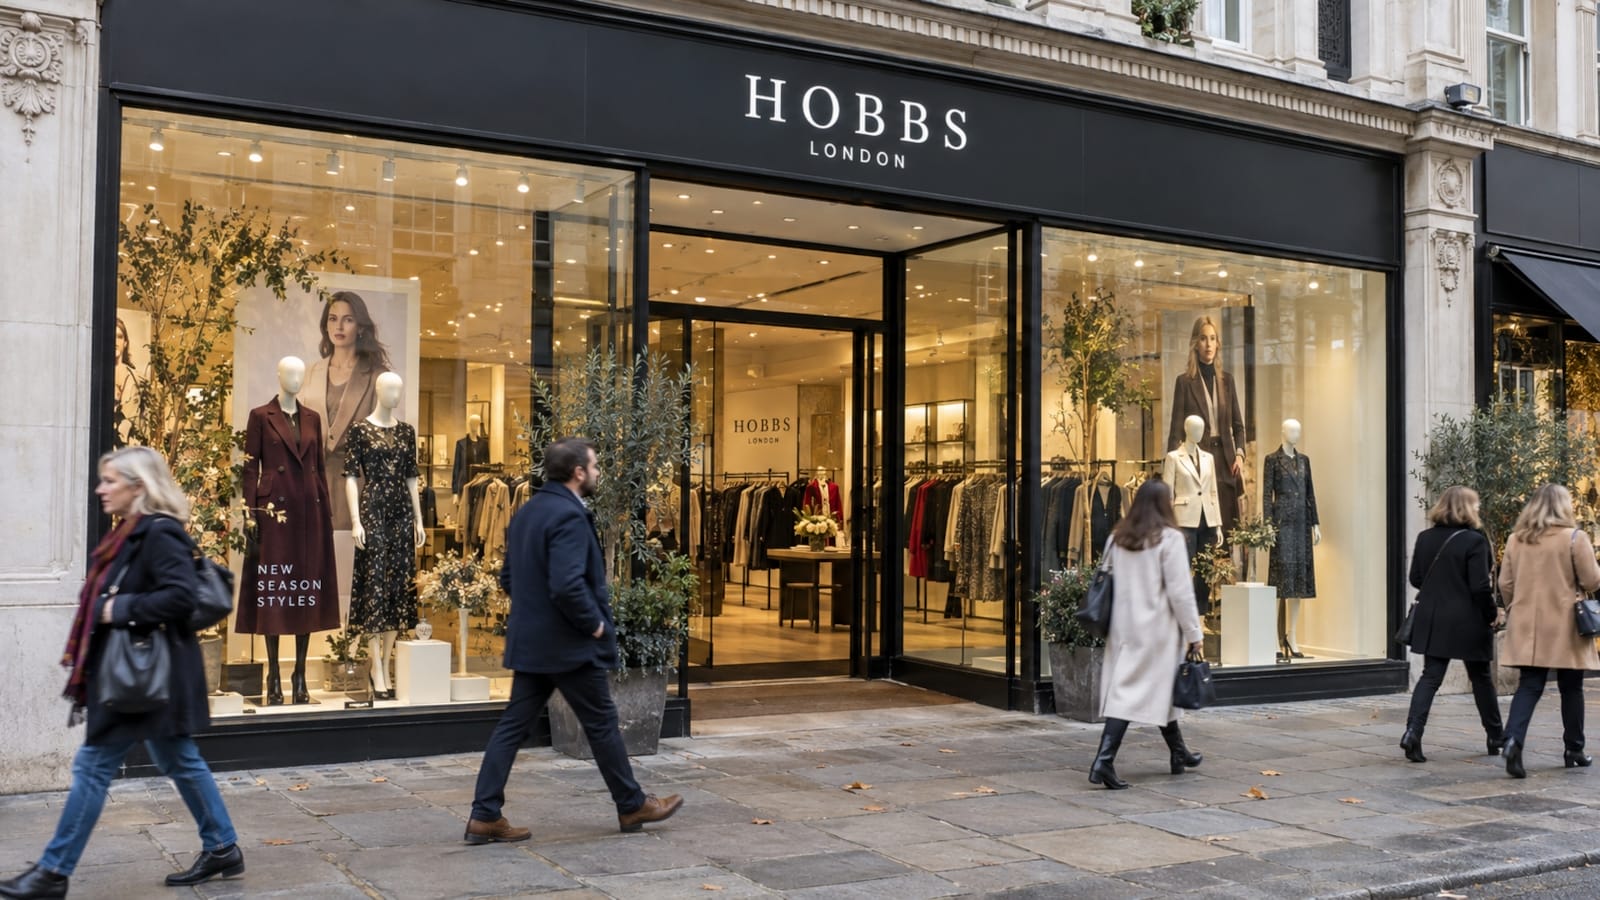
TFG London Cybersecurity Incident Disrupts IT Systems at Phase Eight, Hobbs and Whistles
TFG London has detected a cybersecurity incident affecting IT systems used by the premium fashion brands Phase Eight, Hobbs and Whistles.
The company announced that its physical stores remain open, although some IT systems are still unavailable.
TFG London says other brands and regions are unaffected
According to the company, the incident does not affect its other brands, Inside Story and White Stuff, or its operations in Australia and Africa.
TFG London is the British subsidiary of South Africa’s Foschini Group, which owns the five fashion and homeware brands mentioned above.
As of mid-2026, the group has 649 retail stores worldwide and reported annual sales of £488 million ($646 million).
Cybersecurity investigation is underway
The company detected the cyberattack on October 11, immediately activated its incident response and business continuity plans, and brought in external cybersecurity experts to contain the threat.
TFG London is investigating whether any customer information has been compromised. The company said it will notify affected individuals and organizations if their data has been impacted.
BleepingComputer was unable to find any attackers publicly claiming responsibility for compromising TFG London.
Customers warned to watch for phishing attacks
TFG London is not currently aware of a customer data breach. However, customers of Phase Eight, Hobbs and Whistles are advised to remain vigilant for potential phishing and social engineering attacks.
The incident comes shortly after another British fashion retailer, ASOS, suffered a data breach when hackers sent push notifications to users of its mobile app.
ASOS later confirmed that attackers used social engineering to steal employee login credentials and gain unauthorized access to customer data, including names, contact details and account information.
H&M investigates separate cyberattack claims
Earlier this week, rumors surfaced about an attack on Swedish multinational clothing company H&M. The attackers allegedly claimed that the company had been compromised by the ShinyHunters group and threatened to leak stolen data.
In response to a request for comment, an H&M spokesperson said that current evidence does not indicate a breach, but that the company is investigating the allegations.
An H&M spokesperson told BleepingComputer:
“We are aware of information circulating online regarding a potential cybersecurity incident and are currently investigating the claims.”
“At this time, we have found no indication that our data environment has been compromised.”

Join Mikko Hypponen and security leaders from the NFL, Chanel, and Atlassian for a two-hour digital summit about what will change with AI-speed attacks, what defenders should stop doing, and how to verify, decide, fix, and revalidate at machine speed.
Source: www.bleepingcomputer.com