


Cisco Warns of Critical Secure Email Gateway Zero-Day Exploited in Attacks
Cisco has warned customers to patch a critical zero-day vulnerability in its Secure Email Gateway (SEG) appliances after confirming that attackers are actively exploiting the flaw.
“In September 2026, Cisco PSIRT became aware of active exploitation of this vulnerability,” the company said in a security advisory.
Cisco Secure Email Gateway flaw allows root-level command execution
The vulnerability, tracked as CVE-2026-76461, affects Cisco AsyncOS Software for Cisco Secure Email Gateway. Both virtual and physical appliances are affected, regardless of device configuration.
An unauthenticated, remote attacker could exploit the flaw to execute arbitrary commands with root privileges on the underlying operating system.
“This vulnerability is due to insufficient validation of email parsing logic. An attacker could exploit this vulnerability by sending a crafted email message that contains malicious SQL statements through an affected device,” Cisco said.
“A successful exploit could allow the attacker to execute arbitrary SQL statements, resulting in commands being executed with root privileges on the underlying operating system.”
Administrators urged to check logs for suspicious SQL statements
Cisco shared indicators of compromise and advised network defenders to look for suspicious SQL statements in the mail_log of each cluster device.
Administrators should also review network and firewall logs for signs of suspicious activity, including uploads and downloads to external or malicious IP addresses. Attackers may attempt to remove evidence of their activity from affected devices.
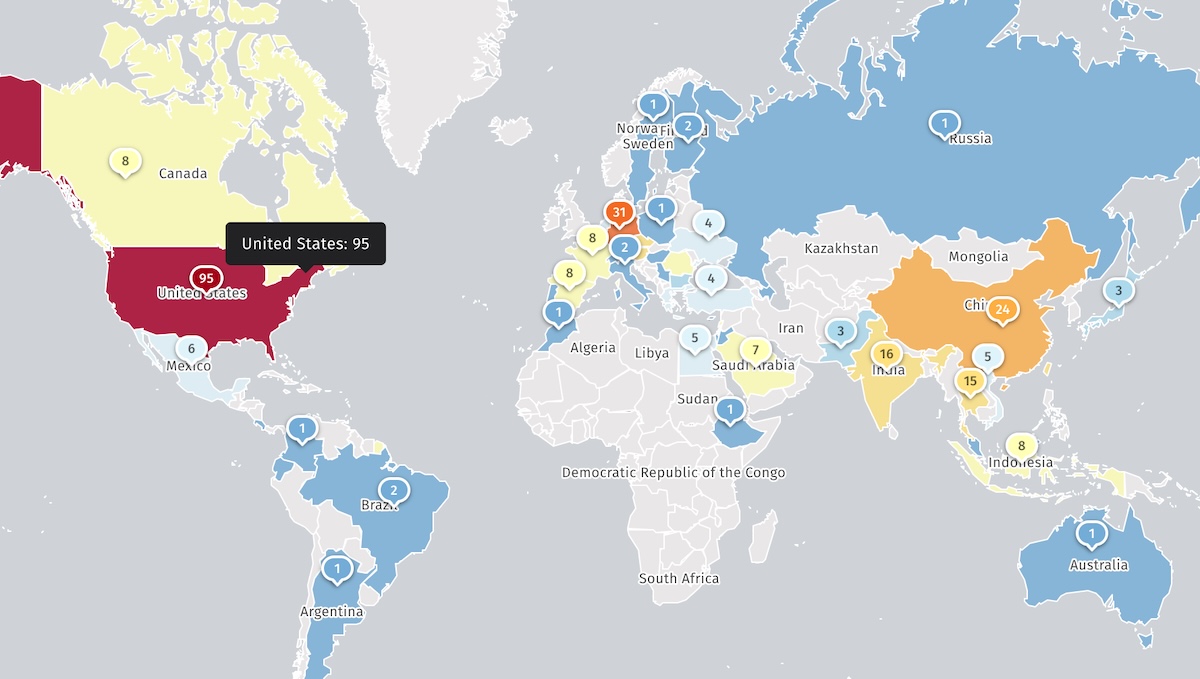
Internet security watchdog Shadowserver is currently tracking more than 400 Cisco Secure Email Gateway appliances. However, it has not provided information about how many of those devices are honeypots or whether they are already protected against attacks.
CISA adds CVE-2026-76461 to its Known Exploited Vulnerabilities Catalog
The Cybersecurity and Infrastructure Security Agency (CISA) also added CVE-2026-76461 to its Known Exploited Vulnerabilities (KEV) Catalog on Monday.
Federal agencies were ordered to patch their systems within three days, by September 17.
Four additional critical Cisco email security flaws disclosed
On Monday, Cisco also disclosed four other critical vulnerabilities affecting Secure Email Gateway and Secure Email and Web Manager (SEWM) appliances, regardless of configuration.
The flaws are tracked as CVE-2026-76440, CVE-2026-76441, CVE-2026-20353, and CVE-2026-76443. Cisco said there is no evidence that these four vulnerabilities have been exploited in the wild.
In January, Cisco patched another maximum-severity AsyncOS vulnerability, CVE-2025-20393, which had been exploited in zero-day attacks against SEG and SEWM devices since November 2025.
Cisco recently revealed that three ransomware and state-sponsored threat groups had exploited vulnerabilities in two recently patched Secure Firewall Management Centers (FMCs).
Since November 2021, CISA has listed 98 Cisco vulnerabilities in its catalog as being actively exploited in attacks. Seven of those vulnerabilities were exploited by ransomware gangs.

Join Mikko Hypponen and security leaders from the NFL, Chanel, and Atlassian for a two-hour digital summit about what will change with AI-speed attacks, what defenders should stop doing, and how to verify, decide, fix, and revalidate at machine speed.
Source: www.bleepingcomputer.com