


ASOS Confirms Data Breach After Hackers Send Fraudulent Push Notifications
British fashion retailer ASOS confirmed a data breach on Tuesday after hackers sent fraudulent push notifications through the company’s mobile app and claimed to have stolen customer data from its Snowflake environment.
ASOS is a leading UK-based online fashion retailer that sells clothing, footwear, accessories and beauty products to customers worldwide, including in the United States.
In a statement, ASOS said that a third-party platform used to communicate with customers may have been accessed without authorization. The company said basic personal information, including names and contact details, may have been compromised.
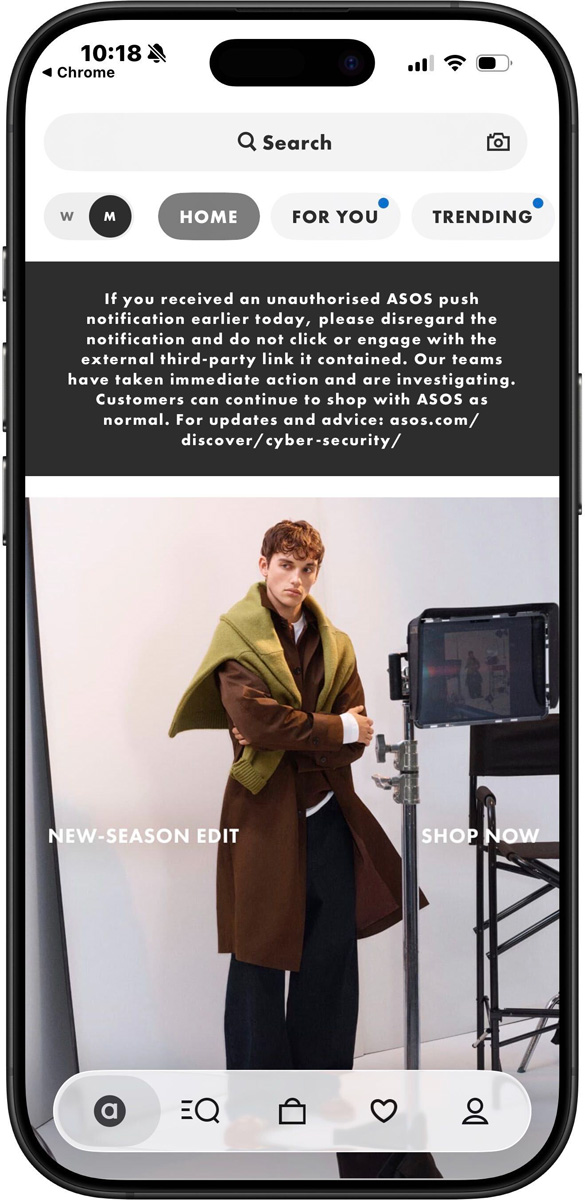
ASOS is now displaying in-app warnings instructing customers to ignore fraudulent push notifications and avoid clicking or accessing any external third-party links included in them.
However, the company has not confirmed the attackers’ claim that its Snowflake environment was compromised. ASOS also has not disclosed how many customers may be affected.
ASOS said it does not believe payment card information or account passwords were impacted.
If you have information about this incident or other undisclosed attacks, please contact us confidentially through Signal at 646-961-3731 or [email protected].
Hackers misuse ASOS mobile app to send breach claims
The fraudulent notifications began appearing at around 5 a.m. ET on Tuesday. Multiple BleepingComputer readers contacted us after receiving the alerts on their phones.
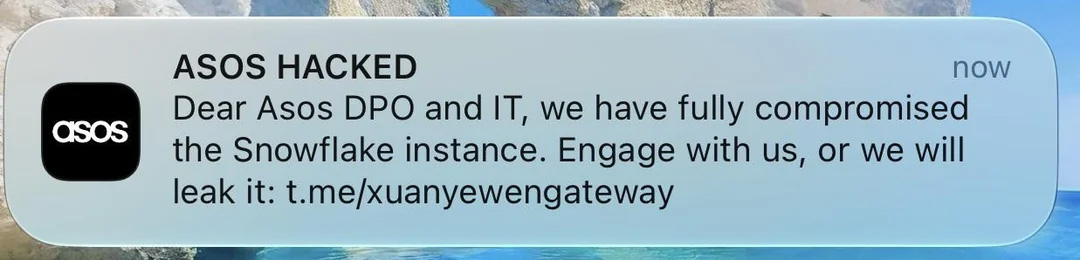
The notification displayed by BleepingComputer read, “ASOS HACKED.”
It continued:
“Asos DPO and IT, we have fully compromised your Snowflake instance. Engage with us or we will leak your information.”
Source: Reddit
Other ASOS customers also reported receiving the same notification on Reddit, suggesting that many, if not all, mobile app users may have received the message.
The notification directed ASOS to a Telegram channel operated by a threat actor group calling itself the “Xuanye Group.”
In a message posted to the channel on Tuesday morning, the attackers claimed that payment information was not affected by the breach.
The attackers later issued a “final statement” claiming that they had stolen customer information.
“The affected organization’s apps are safe to use. This incident contains customer information, which is safe on our servers and will not be touched for a specified period of time,” the group said.
“Given the current climate regarding incident disclosure in the cybersecurity industry, we believe you will appreciate our generous clarity regarding this incident.”
The group did not specify what customer information was allegedly stolen or how many customers were affected. It also did not provide evidence that ASOS’ Snowflake environment had been compromised.
BleepingComputer attempted to contact the threat actor about the alleged breach. The threat actor requested payment, but we did not proceed because paying for information violates our editorial guidelines.

Join Mikko Hypponen and security leaders from the NFL, Chanel, and Atlassian for a 2-hour digital summit about what will change with AI speed attacks, what defenders should stop doing, and how to verify, decide, fix, and revalidate at machine speed.
Source: www.bleepingcomputer.com