


UpdraftCentral Key Compromise Puts Up to 400,000 WordPress Sites at Risk
A threat actor compromised the website of TeamUpdraft, the developer of the popular WordPress backup and security plugin UpdraftPlus. The attackers also compromised UpdraftCentral connection keys, potentially allowing them to send commands to connected WordPress websites.
TeamUpdraft detected unauthorized access to its infrastructure during the weekend of October 17 and 18. The company believes the attackers gained access to its customer database, which contained customer and billing details, order history, password hashes, two-factor authentication setup information, and connection keys for its services.
TeamUpdraft develops several WordPress tools for backups, cloud storage, staging, and remote site management:
- UpdraftPlus: A WordPress backup and restore plugin with more than 4 million downloads.
- UpdraftCentral: A service for managing multiple WordPress sites remotely.
- UpdraftVault: Cloud backup storage.
- UpdraftClone: A service for creating staging websites.
TeamUpdraft says customer data may have been accessed
In an October 2026 security advisory, TeamUpdraft said it observed unauthorized access to the teamupdraft.com website during the weekend of October 17 and 18.
“Our teams responded quickly and worked through the night to contain it. We closed the access route, signed out all accounts, and replaced keys and credentials that may have been affected,” the company said.
The vendor said it does not store payment details and that UpdraftPlus plugin files and downloads remain unaffected. Self-hosted UpdraftCentral instances are also not affected.
However, the company recommends that users rotate their remote storage credentials and re-authenticate their connections if they access a website through UpdraftCentral. Backups stored in a customer’s own remote storage are not believed to be affected.
Stolen UpdraftCentral keys used to install WordPress backdoors
An estimated 10% of websites using UpdraftPlus have an UpdraftCentral or Migrator key. This could expose approximately 400,000 websites to attacks using stolen connection keys.
According to Oliver Sild, lead researcher at Patchstack, attackers have begun using stolen access keys to backdoor websites connected to UpdraftCentral. Sild said the campaign could be more serious than the “wp2shell” attack.
Patchstack reported that the attack began on October 18 at 15:32 UTC. The attackers were able to run arbitrary code and create WordPress accounts with full administrator privileges.
Researchers documented at least 99 malicious backdoor plugins with distinct names designed to masquerade as WordPress maintenance and optimization tools, including “Site Health Cache.”
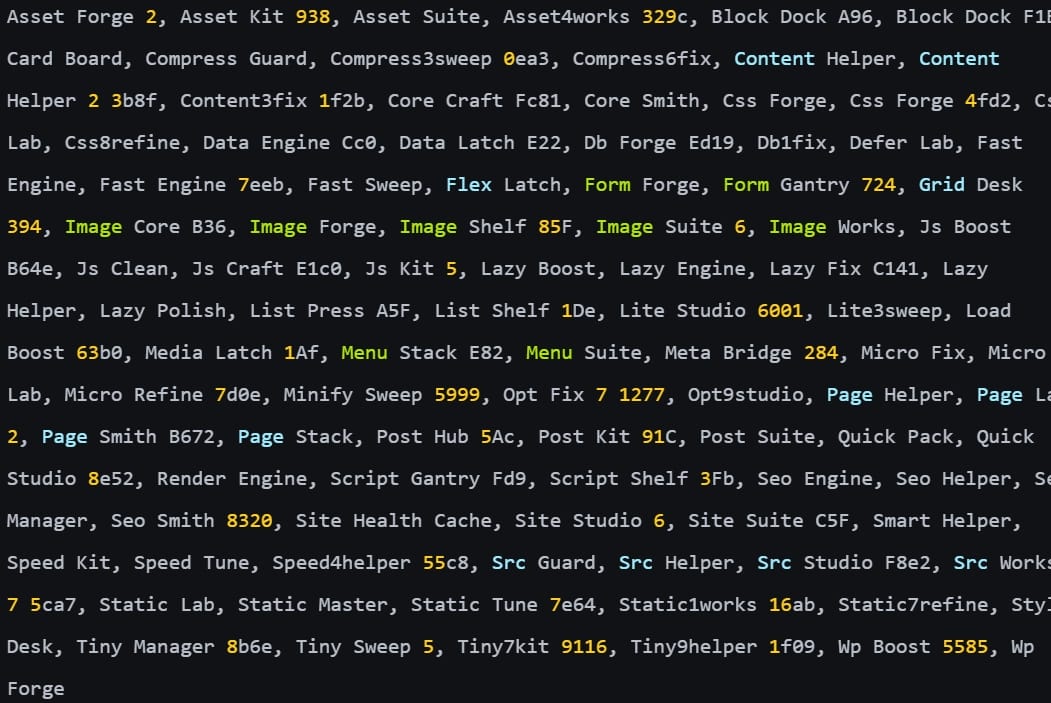
Source: Patchstack
Patchstack described an early version of the backdoor plugin that did not work because of a coding error. However, a report from web application security firm Nethemba describes a newer version capable of creating privileged accounts or logging in as existing WordPress administrators.
Nethemba said three of its WordPress websites were targeted through UpdraftCentral, and two were successfully infected with malicious plugins.
“All three sites are running current WordPress 7.1.3 and UpdraftPlus 2.26.11, which has been patched for the June vulnerability CVE-2026-10795,” Nethemba said.
“The attacker did not compromise our servers or exploit weaknesses in our configuration. The attacker gained entry through the UpdraftCentral remote administration channel and signed commands using a valid Dashboard private key.”
UpdraftPlus users should update and delete connection keys
Nethemba reported that TeamUpdraft’s initial UpdraftPlus 1.26.12 and 2.26.12 releases were intended to remove UpdraftCentral Cloud keys, but a bug prevented the keys from being removed correctly.
Users should update UpdraftPlus to the following versions or later:
- UpdraftPlus Free: 1.26.13 or later
- UpdraftPlus Premium: 2.26.13 or later
After updating, administrators should log in to each WordPress site and delete the UpdraftCentral connection key by navigating to:
Settings → UpdraftPlus Backup → Advanced Tools → UpdraftCentral → Manage Existing Keys
Administrators should also inspect their logs and files for indicators of compromise using the guidance published by TeamUpdraft, Patchstack, and Nethemba.
If a compromise is confirmed, restore the website from a clean backup, change the TeamUpdraft account password, cancel all active sessions, and reset the two-factor authentication protection methods.

The overall prevention score can hide what happens after the initial access. If an attacker uses valid credentials, your defenses drop sharply.
The Blue Report 2026 measures defense techniques by technology across 338 million simulations run in customer production environments.
Source: www.bleepingcomputer.com