


Cybersecurity company ReliaQuest has confirmed that an employee was targeted in a social engineering attack after a threat actor impersonated a member of the company’s security team.
In a statement issued over the weekend, ReliaQuest said the attacker called multiple employees and attempted to persuade them to visit a fake ReliaQuest single sign-on (SSO) page hosted behind a content delivery network.
Last week, ReliaQuest’s threat research team warned that the ShinyHunters extortion group was registering .claims domains to impersonate company help desks and IT departments. The original posts have since been deleted: view the archived posts.
“ReliaQuest is tracking a wide range of ShinyHunters campaigns using domains that follow the company[.]complaint pattern. These domains incorporate the target organization’s name or abbreviation under the .claims TLD,” the company said in a post on X.
On the following day, a newly created X account believed to be associated with the threat actor responded to ReliaQuest’s warning, asking, “Who’s hunting whom?” The account also shared a screenshot that appeared to show a compromised ReliaQuest employee’s Okta SSO account: view the post.
Shortly afterward, ShinyHunters published the same screenshot in a new entry on its data extortion website.
Both ReliaQuest’s post and the alleged threat actor’s post were later removed from X.
According to ReliaQuest, the attackers hosted phishing pages on look-alike domains. Sources told BleepingComputer that one such domain was reliaquest.claims. During the voice phishing, or vishing, attempt, the attackers also used the name of a legitimate ReliaQuest security employee.
One targeted employee entered their credentials on the fake SSO page and approved an MFA push notification. This gave the attacker temporary, view-only access to ReliaQuest’s identity dashboard.
However, ReliaQuest said its device trust controls blocked subsequent attempts to access applications through the dashboard.
“The scope of access was for viewing only. No ReliaQuest applications or systems were accessed, and no customer data was touched,” ReliaQuest said.
“The attackers continued to attempt to access these applications through the dashboard, but were consistently denied due to security controls in place.”
The company terminated the attacker’s session, revoked the exposed password, and reset all authentication tokens.
A subsequent investigation found no evidence that the attackers accessed other accounts, applications, or data. ReliaQuest also found no indication that the threat actors established persistence within its systems.
ReliaQuest said it has audited control fidelity, device reliability, and network access since August 21 and has not identified any suspicious activity.
ShinyHunters claims ReliaQuest attack
ReliaQuest’s statement came shortly after the notorious data extortion group ShinyHunters claimed to have compromised the company.
In a new post on its extortion portal, ShinyHunters referenced ReliaQuest’s earlier report about the group, writing, “This post… you not us.”
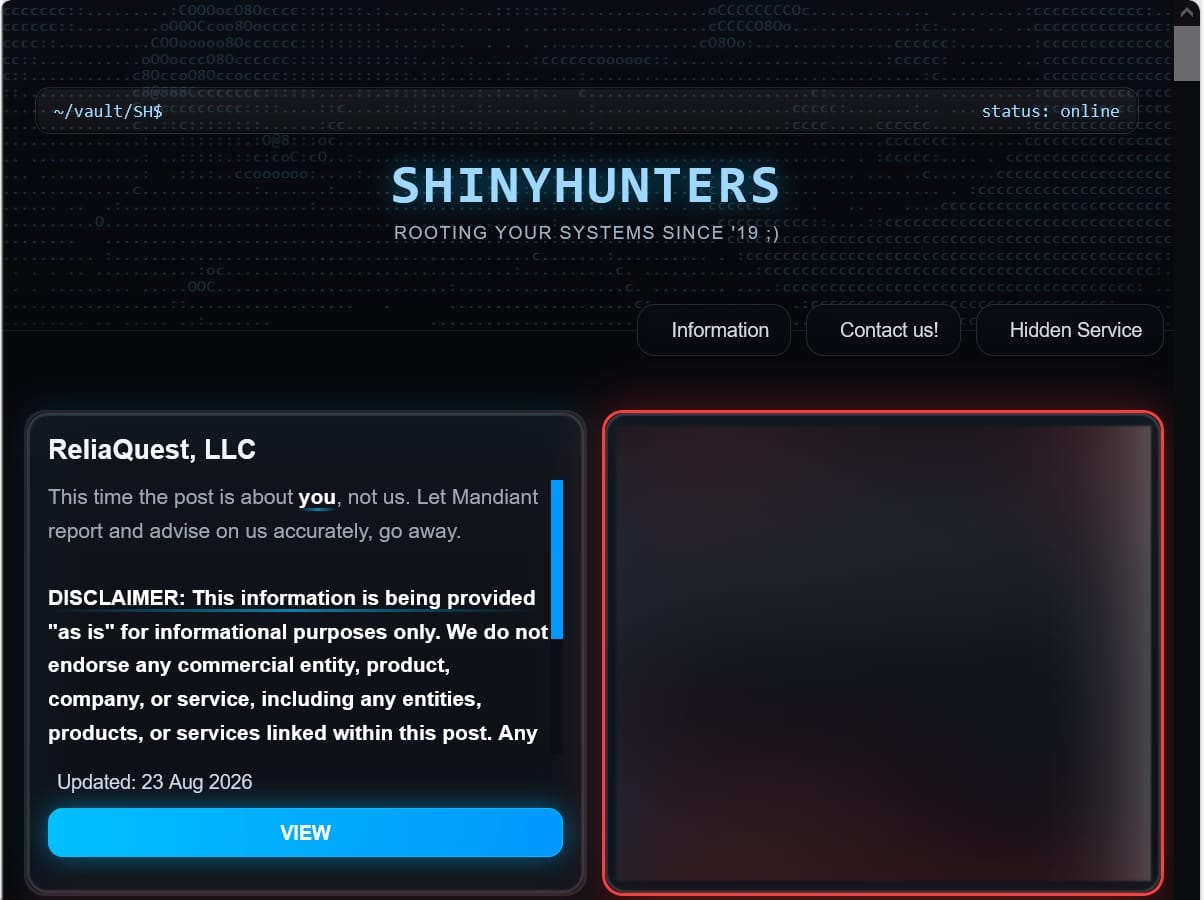
Source: BleepingComputer
The attackers published what they described as evidence of access, including a screenshot showing a compromised ReliaQuest Okta SSO account.
BleepingComputer asked ReliaQuest whether the incident was connected to ShinyHunters, but the company has not provided additional information.
However, ShinyHunters told BleepingComputer that the access was limited to viewing information and did not provide access to applications, systems, or customer data.
“There is no access to additional identities, no access to business applications, no access to customer data or ReliaQuest data beyond the user’s login credentials, and no persistence is established,” the attacker said.

The overall prevention score can hide what happens after initial access. When attackers use valid credentials, the effectiveness of security defenses can drop sharply.
Blue Report 2026 measures defense techniques across technologies using 338 million simulations conducted in customer production environments.
Source: www.bleepingcomputer.com