


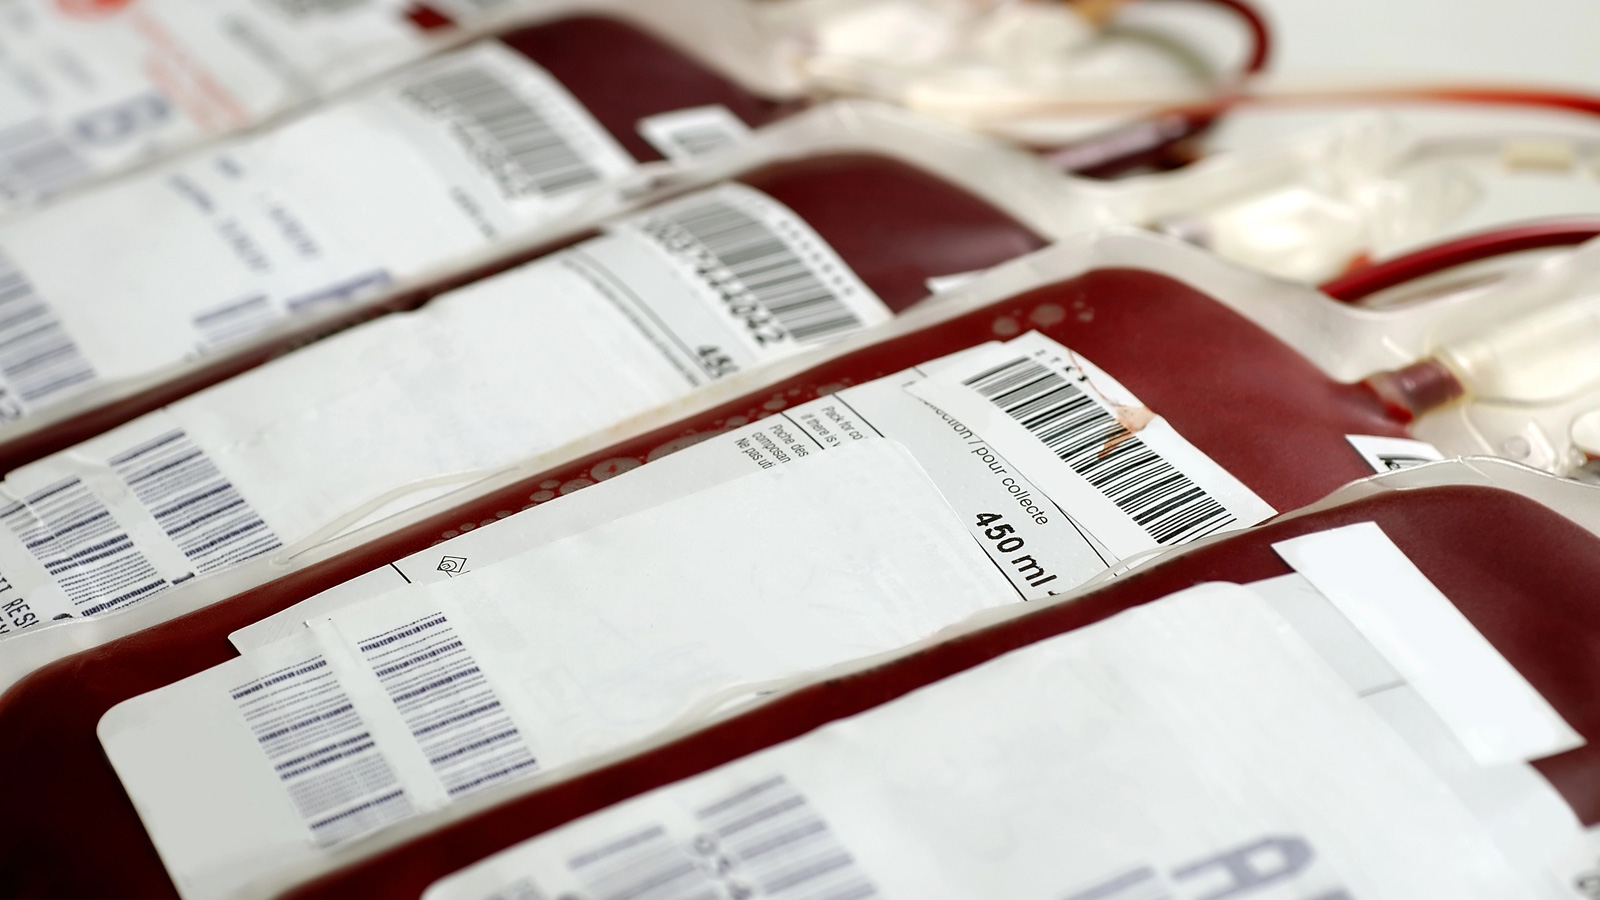
France’s national blood service, the Établissement français du Sang (EFS), says a cyberattack on a refrigeration equipment provider altered temperature and defrost settings at three facilities, putting stored blood products and biological samples at risk. The incident occurred on November 2, but monitoring and alarm systems detected the changes quickly, and EFS said no health effects or loss of blood products have been reported.
Cyberattack affected refrigeration controls
EFS manages blood collection, processing and distribution across France. In a statement published on November 3, the organization said it was not the direct target of the attack. Instead, the incident affected one of its refrigeration equipment providers and the system used to monitor and control cold rooms.
EFS did not identify the supplier. However, European refrigeration equipment provider Coolworld Rentals confirmed that a limited number of its refrigeration units were affected by a cybersecurity incident involving remote monitoring software.
Coolworld said the attackers exploited vulnerabilities in third-party components outside the company’s direct control.
“The vulnerabilities currently reported in the media were related to components from third-party suppliers and were outside of Coolworld’s direct control,” the company said.
“Only a limited number of Cool World units were affected and Cool World responded quickly and took appropriate measures.”
The company said it is working with affected customers but does not comment on individual cases.
EFS moved or secured affected products
At EFS, the incident caused temperatures and defrost thresholds in affected cold rooms to rise to extremely high levels. The facilities store blood products and biological samples before they are shipped to hospitals.
EFS said its monitoring and alarm systems quickly detected the temperature changes. Staff then repaired affected equipment or moved products to other cold-storage facilities.
“No health effects have been identified and no loss of blood products has been reported,” EFS said in a statement translated from French.
The organization added that plasma bags intended for transfusions, along with plasma used to manufacture medicines, were transferred or secured to prevent damage. Blood collection and distribution operations continued without interruption.
EFS said its technical team is working with the French National Cyber Security Agency (ANSSI) and the Ministry of Health to strengthen monitoring of refrigeration equipment and temperatures.
Attacks have targeted refrigeration systems across Europe
The incident follows a wave of cyberattacks targeting refrigeration systems across Europe. In these attacks, threat actors remotely changed temperature settings or activated defrost functions that stopped cooling.
In October, a cyberattack disrupted refrigeration systems at an estimated 250 to 350 French supermarkets, including Intermarché, Carrefour Market, Monoprix, Leclerc and Super U. Hackers reportedly compromised refrigeration controllers running outdated Danfoss software and remotely triggered automatic defrost functions, increasing temperatures and forcing stores to discard fresh and frozen products.
The targeted systems included Danfoss AK-SM/AK-SC and Copeland/Dixell XWEB refrigeration controllers, which are used to remotely monitor and manage chillers.
A second wave of attacks occurred this month, affecting more than 115 stores in Belgium, the Netherlands, Sweden, Luxembourg, Ireland and Estonia. Some refrigeration systems shut down completely, while attackers remotely changed temperature settings in others.
One Swedish supermarket reported that its system began heating up, while another store’s temperature was changed to 50°C (122°F).
Belgian refrigeration company Subcobel previously said the attackers behind the November incident exploited the same vulnerability used in an October attack on a French supermarket.
Vulnerabilities in Danfoss controllers remain unconfirmed as the cause
In 2025, the U.S. Cybersecurity and Infrastructure Security Agency (CISA) disclosed two vulnerabilities affecting Danfoss AK-SM 8xxA controllers. The flaws are tracked as CVE-2025-41450 and CVE-2025-41451.
The vulnerabilities could allow an attacker to bypass authentication and remotely execute commands on a vulnerable system, potentially taking control of refrigeration equipment.
However, it has not been confirmed whether these vulnerabilities were exploited in the attacks described above.
Source: www.bleepingcomputer.com