


Citrix Urges Immediate Patching of Critical NetScaler Vulnerability CVE-2026-107406
Citrix is urging IT administrators to immediately patch NetScaler ADC networking appliances and NetScaler Gateway secure remote access solutions against a new critical vulnerability that could allow remote code execution (RCE) or cause a denial-of-service condition.
Critical NetScaler flaw could enable remote code execution
Tracked as CVE-2026-107406, the vulnerability is caused by a memory overflow issue. An attacker could exploit the flaw to execute code remotely on a targeted appliance or trigger a denial-of-service condition that causes the device to crash.
The vulnerability affects NetScaler ADC and NetScaler Gateway appliances configured as Security Assertion Markup Language (SAML) identity providers (IdPs) or service providers (SPs).
Citrix said it is not aware of any unmitigated exploitation of CVE-2026-107406 at the time of publishing its security bulletin.
“We strongly encourage affected customers to review the advisory and upgrade their affected NetScaler instances to the recommended version as soon as possible,” the company said.
Citrix NetScaler versions affected by the vulnerability
Citrix advised customers to upgrade vulnerable NetScaler ADC and NetScaler Gateway appliances to the following versions:
- NetScaler ADC and NetScaler Gateway 14.1-73.46 and later
- NetScaler ADC and NetScaler Gateway 13.1-64.29 and later 13.1 releases
- NetScaler ADC 14.1-FIPS 14.1-73.46 FIPS and later 14.1-FIPS releases
- NetScaler ADC 13.1-FIPS and 13.1-NDcPP 13.1.37.283 and later 13.1-FIPS and 13.1-NDcPP releases
More than 21,000 NetScaler systems exposed online
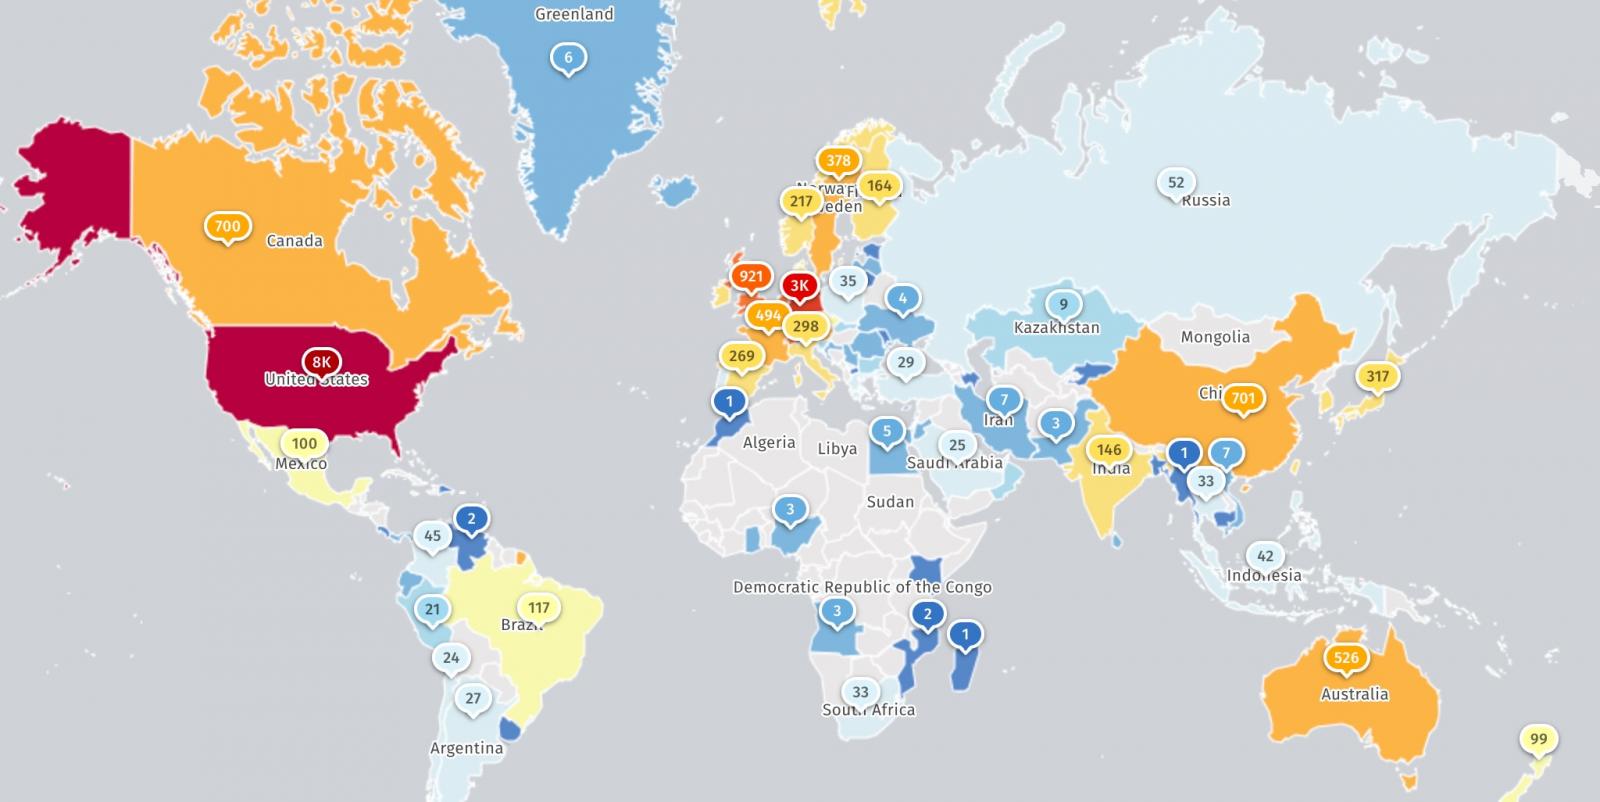
Internet threat-monitoring organization Shadowserver tracks more than 21,000 IP addresses associated with NetScaler devices exposed to the internet. This includes just over 1,500 NetScaler Gateway instances and approximately 20,000 NetScaler ADC appliances.
However, there is currently no information about how many of those systems are honeypots, how many have already been patched, or how many use configurations vulnerable to CVE-2026-107406.
Citrix NetScaler vulnerabilities have been exploited
Although Citrix has found no evidence that attackers have begun exploiting CVE-2026-107406 in the wild, the company has warned of other NetScaler vulnerabilities exploited by attackers since the beginning of the year.
In March, Citrix urged customers to patch two additional NetScaler security issues, CVE-2026-3055 and CVE-2026-4368, amid warnings that attackers could begin exploiting them.
Most recently, in September, Citrix released security updates for two aggressively exploited NetScaler RCE zero-days, CVE-2026-88771 and CVE-2026-88772. The vulnerabilities allowed attackers to deploy custom web shells and tunneling malware, steal credentials, gain root access, and move into victims’ internal networks.
Earlier this month, Citrix issued an emergency update to address CVE-2026-88779, a zero-day denial-of-service vulnerability in NetScaler. Researchers and administrators later reported that the flaw could also be exploited to achieve remote code execution.
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has reported 27 Citrix vulnerabilities as actively exploited, including seven that have been exploited in ransomware attacks since November 2021.

Join Mikko Hypponen and security leaders from the NFL, Chanel, and Atlassian for a two-hour digital summit about what will change with AI-speed attacks, what defenders should stop doing, and how to verify, decide, fix, and revalidate at machine speed.
Source: www.bleepingcomputer.com