


Google Pauses Open Source Bug Bounty Submissions After Flood of AI-Generated Reports
Google has temporarily suspended new submissions to its Open Source Software Vulnerability Rewards Program (OSS VRP) after being inundated with ineffective, AI-generated vulnerability reports.
Why Google paused its OSS vulnerability rewards program
The OSS VRP encourages security researchers to responsibly disclose vulnerabilities in open source projects managed by Google. These projects include Golang, Angular, Bazel, Protocol Buffers, and Fuchsia, along with critical third-party dependencies.
The program also covers security issues involving repository settings, including GitHub Actions, application configurations, and access control rules.
Google launched the OSS VRP in August 2022, offering rewards ranging from $100 to $31,337. The program was designed to focus on vulnerabilities with the greatest potential impact on the software supply chain.
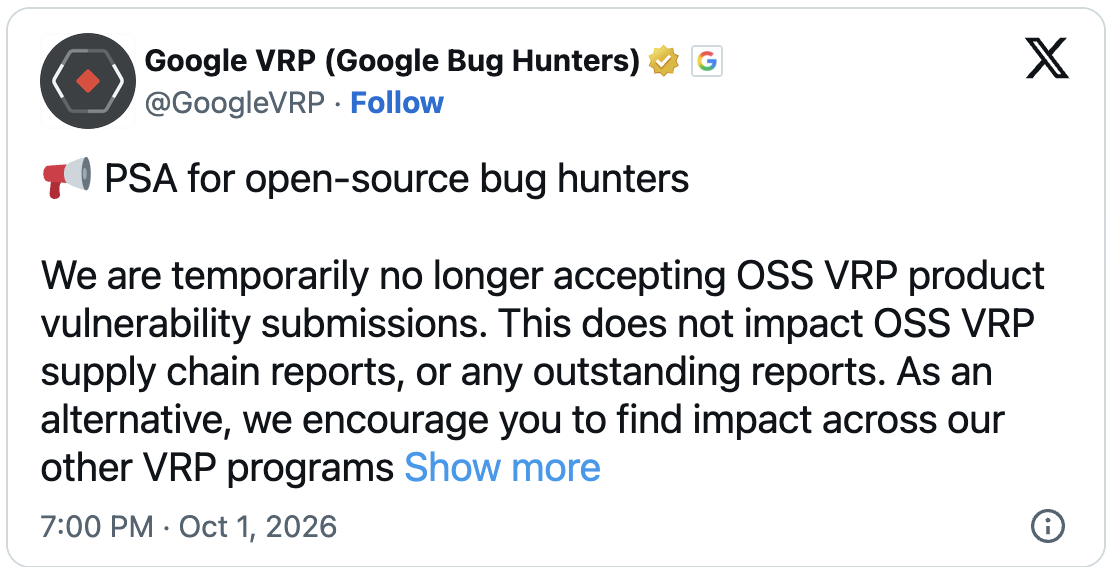
“We have temporarily stopped accepting submissions regarding vulnerabilities in OSS VRP products. This does not affect OSS VRP supply chain reports or open reports,” Google said.
“Why is this happening? This pause is due to a significant increase in automated submissions, the majority of which are ineffective.”
Google will update the program in 2027
Google said it is retuning the OSS VRP to address the increase in automated submissions. The company plans to provide more information about the changes in the first quarter of 2027.
“We continue to reformat OSS VRP and work on this aspect and are committed to delivering an update in Q1 2027,” Google said in an update to the Bug Hunters website.
Google added that the change does not affect vulnerabilities in products submitted before October 1, 2026.
Researchers can still submit security patches for open source software through the Google Patch Rewards Program, which offers rewards of up to $15,000 for high-impact fixes. They can also report vulnerabilities in Google Cloud open source repositories that affect cloud products through Google’s Cloud VRP.
“In the meantime, we encourage you to find the impact across our other VRP programs and submit there instead, or pursue the Patch Rewards Program,” Google said.
Google has awarded more than $81.6 million to security researchers
Since launching its first Vulnerability Rewards Program in 2010, Google has awarded more than $81.6 million to thousands of security researchers.
In 2025, Google awarded a record $17.1 million to more than 700 security researchers. That was a 40% increase from 2024, when the company awarded a total of $12 million.
AI-generated vulnerability reports are overwhelming bug bounty programs
Google is not the first organization to change its bug bounty program after being overwhelmed by a continued barrage of low-quality reports generated with AI tools.
In January, the administrators of the curl command-line utility and library ended the project’s HackerOne security bug bounty program after receiving a large volume of AI-generated vulnerability reports.
More recently, in mid-September, Intel removed financial compensation for security flaws in software, firmware, hardware, and services reported through the Intigriti Bug Bounty Program. Intel has not explained the decision.
Microsoft has not made a similar move, but the company warned in May that AI tools will help uncover far more vulnerabilities, resulting in “a greater pace and breadth of vulnerability discovery.”
Microsoft said the trend is increasing across the software industry and will likely increase operational demands. Last month, the company released patches for a record 966 flaws, including two actively exploited zero-day vulnerabilities.

Join Mikko Hypponen and security leaders from the NFL, Chanel, and Atlassian for a two-hour digital summit about what will change with AI-speed attacks, what defenders should stop doing, and how to verify, decide, fix, and revalidate at machine speed.
Source: www.bleepingcomputer.com