


Check Point Patches Critical Vulnerability Allowing Root-Level Remote Code Execution
Check Point Software has released a security update for a critical vulnerability that could allow attackers to execute code with root privileges on affected systems.
CVE-2026-91843 affects Check Point management servers
Tracked as CVE-2026-91843, the flaw is caused by a stack-based buffer overflow in the login process of Check Point Security Management Server.
Security Management Server instances manage Check Point security gateways, including firewalls, and monitor network security events. The vulnerability also affects Check Point Log Server, which collects and stores logs generated by the company’s firewalls.
A successful exploit could allow an unauthenticated or unprivileged attacker to execute code remotely with root privileges. The attack is considered low complexity and does not require user interaction.
Temporary mitigation for CVE-2026-91843
Check Point has provided temporary mitigation guidance for customers who cannot immediately deploy the latest LivePatch. Administrators should harden vulnerable systems and restrict access to trusted IP addresses or subnets.
In the SmartConsole Dashboard, administrators can review the settings under Administration and Permissions > Trusted Clients and update the trusted client entries to limit access.
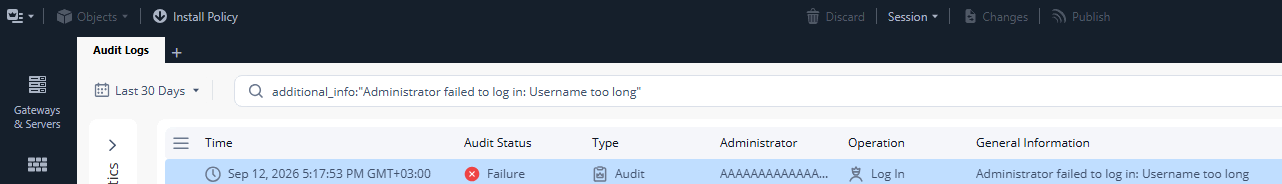
Check Point has not reported that CVE-2026-91843 is being actively exploited. However, the company said its security team can identify attacks by reviewing audit logs and administrator login logs for the following alert:
“Administrator login failed: Username too long”
Additional critical Check Point vulnerabilities patched
Last week, Check Point patched another critical remote code execution flaw, CVE-2026-85103. The vulnerability is caused by a heap overflow in the VPN certificate ASN.1 decoding process and affects Check Point firewalls and management systems.
“Regardless of configuration, all Security Management Server deployments are vulnerable,” Check Point warned. “This vulnerability is not dependent on any specific management configuration. Management is vulnerable even if a VPN is not used or configured.”
On the same day, Check Point disclosed another major vulnerability, CVE-2026-85102, which allows unauthenticated attackers to bypass authentication and execute code remotely on vulnerable firewalls.
Previously exploited Check Point zero-days
Although the latest vulnerabilities have not been exploited in the wild, Check Point reported that other flaws have been actively exploited in recent months.
The first authentication-bypass zero-day, CVE-2026-50751, has been exploited by Qilin ransomware affiliates since June. A second authentication-bypass zero-day, CVE-2026-16232, has reportedly been exploited since at least July to authenticate with administrative privileges to the SmartConsole administration panel.
More recently, the Netherlands National Cyber Security Centre (NCSC-NL) warned organizations to prioritize patching two critical Check Point VPN flaws, CVE-2026-85102 and CVE-2026-85103, stating that “exploitation attempts are expected to occur soon.”

Join Mikko Hypponen and security leaders from the NFL, Chanel, and Atlassian for a 2-hour digital summit about what will change with AI speed attacks, what defenders should stop doing, and how to verify, decide, fix, and revalidate at machine speed.
Source: www.bleepingcomputer.com