


Microsoft Teams to Add AI-Powered Phishing Detection for External Chats
Microsoft Teams will begin using AI-powered phishing detection in early November 2026 to identify malicious behavior in messages, according to Microsoft.
The feature is expected to roll out through a targeted release phase ending in mid-November. Microsoft expects the new security protections to become generally available worldwide between early and mid-December.
Teams will analyze conversation context for phishing threats
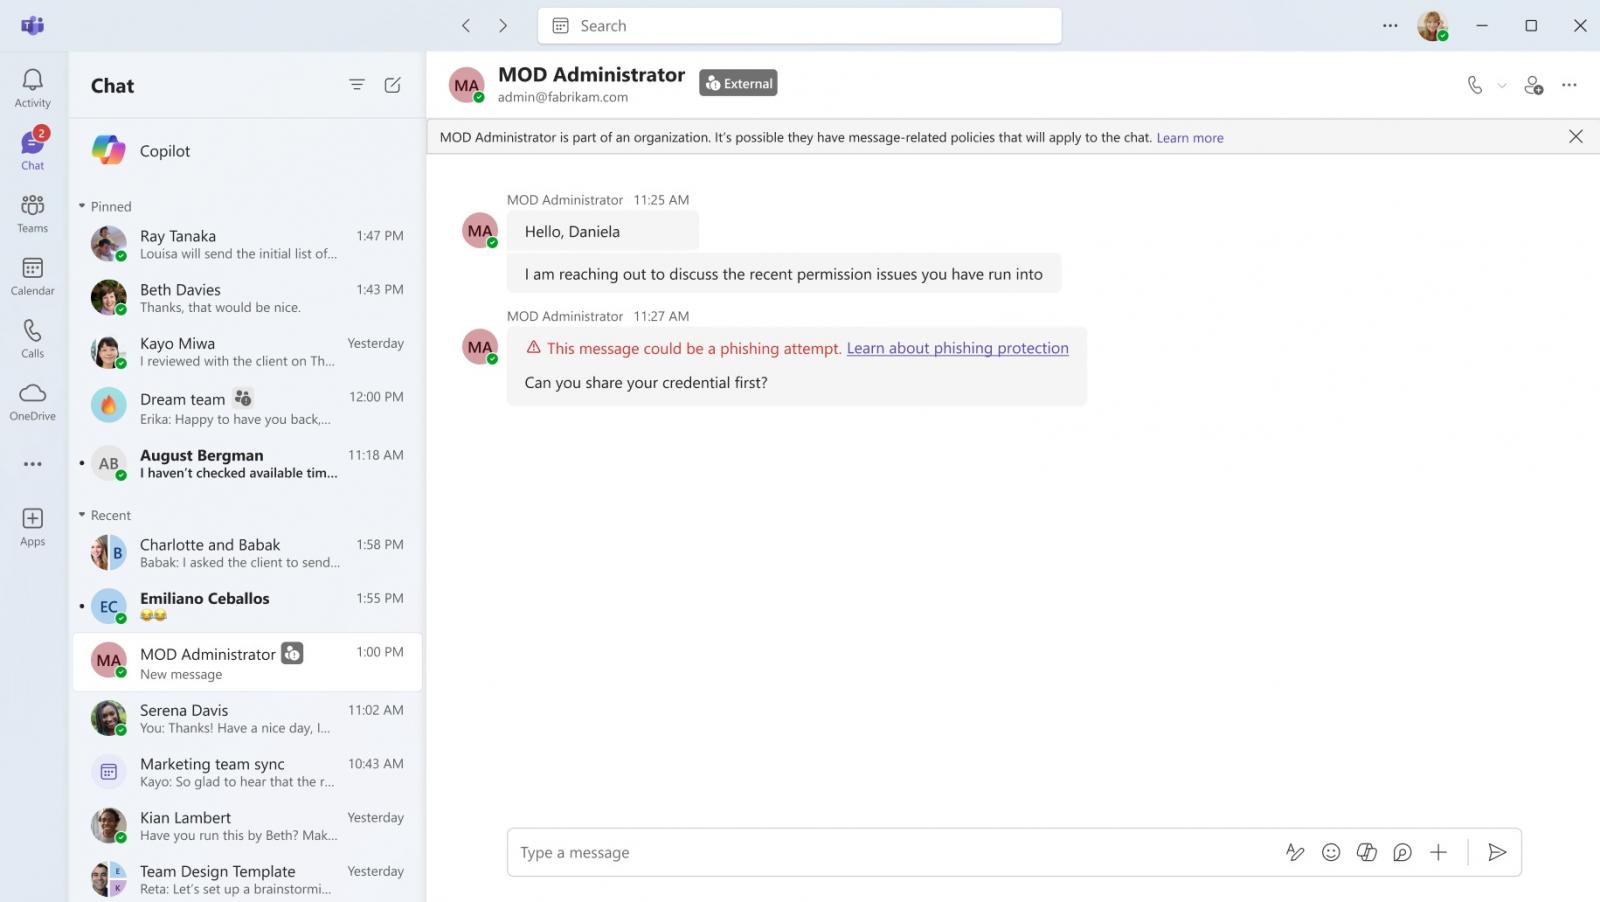
Microsoft first revealed the feature in a Microsoft 365 roadmap entry last week. The AI-powered phishing detection system will use conversation context, without retaining message content, to identify phishing and suspicious behavior in high-risk messaging scenarios such as chats with external users making first contact.
“Microsoft Teams is introducing AI-powered, context-aware phishing detection to help identify phishing, social engineering, impersonation attempts, and deceptive intent,” Microsoft said in a Microsoft 365 Message Center update on Wednesday.
“This feature analyzes the context of a conversation and identifies suspicious behavior that may not include traditional indicators such as malicious links or files.”
Microsoft says IT administrators will not need to take any action to enable the new security protections. For most users, the feature will focus on first-contact chats from external users.
Microsoft says Teams messages will not be retained for AI training
The new Teams security feature will analyze conversation context to detect suspicious behavior, but Microsoft says it will not retain customer data for additional AI training or other uses.
“This feature is used for security purposes only and not for productivity, summarization, advertising, user monitoring, or other non-security purposes,” Microsoft said. “The content of customer messages is not retained by the detection system for model training or other secondary use.”
Teams security updates target external threats
The AI-powered phishing detection feature is part of a broader series of security changes for Microsoft Teams. In December, Microsoft announced that administrators would be able to block external users through the Defender portal starting in January. The change is designed to prevent cybercrime groups, including ransomware gangs, from exploiting Teams for social engineering attacks against employees.
Microsoft also began rolling out new Teams meeting protection policies in August. These policies allow administrators to automatically block all identified external bots from joining meetings.
Last month, Microsoft announced additional protections against fraud and phishing attempts. Teams can now blur QR codes sent by external senders. Users can also report suspicious guest invitations directly in Teams, enabling security teams to block phishing and other attacks that abuse guest invitations.
Most recently, in early October, Microsoft announced plans to add third-party deepfake detection solutions and support for impersonation protection in Teams meetings.

The overall prevention score can hide what happens after the initial access. If an attacker uses valid credentials, your defenses drop sharply.
The Blue Report 2026 measures defense techniques by technology across 338 million simulations run in customer production environments.
Source: www.bleepingcomputer.com