


GMO Group has urged customers of its Onamae Desktop Cloud service in Japan to disconnect their computers from the internet, shut them down and unplug them after an attacker threatened to deploy ransomware. The company has since confirmed that data belonging to GMO and its customers was made publicly available online, although it appears the ransomware was not activated on customer machines.
Onamae Desktop Cloud is a popular VPS provider operated by GMO Internet, a member of the GMO Internet Group and one of Japan’s largest domain registrars.
GMO said it detected an intrusion on October 20 that may have resulted in malware being installed on as many as 26,739 customer servers. To reduce the risk of further compromise, the company shut down its servers and limited service availability while it investigated the incident.
The company said no payment information had been compromised. However, it warned that MetaTrader 4 and MetaTrader 5 (MT4/MT5) credentials and trading account details may have been leaked or compromised. Customers were advised to reset their passwords and terminate any active sessions.
Attackers demanded an 8 billion yen ransom
In an October 24 update, GMO confirmed that data had been stolen. The attackers demanded a ransom of 8 billion yen, or approximately $50 million, but GMO said it would not pay. Instead, the company said it would compensate each customer 5,000 yen, or about $30, for the inconvenience caused.
On October 26, GMO warned that the attackers planned to publish customer information online and install a ransomware payload on customer servers during the early stages of the attack.
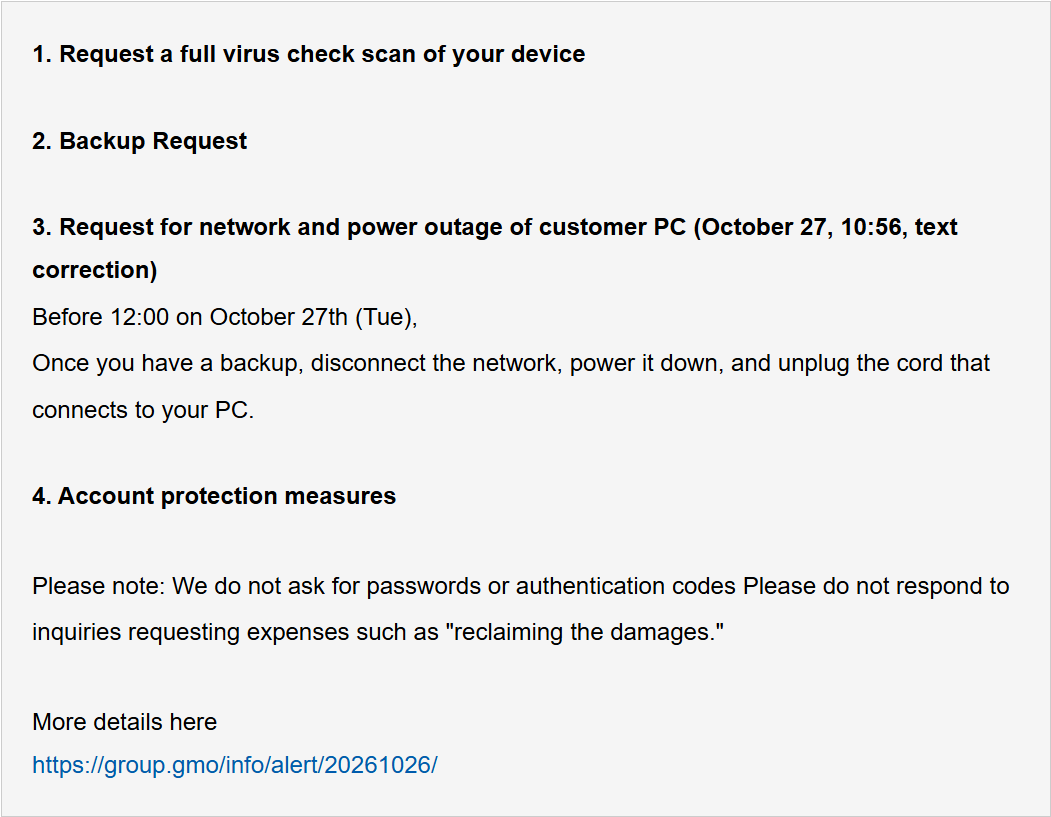
The following day, GMO asked customers to disconnect their PCs. By noon, the company said it had shut down its network and removed all cables while working with Trend Micro to recover from the cyberattack.
“Once you have a backup, disconnect from the network, turn off the power, and unplug the cord connected to your PC,” GMO advised customers.
Source: GMO
GMO said it is scanning customer systems to determine whether malware remains present. It is also offering comparable replacement PCs to customers affected by ransomware attacks.
Company and customer data published online
In a report published earlier on October 27, GMO confirmed that company and customer data had been made publicly available. The company said it was working to verify the reliability of the leaked information.
GMO said it would consider providing additional financial compensation to customers whose information was exposed.
Although the attackers threatened to launch ransomware, it appears they did not follow through. GMO said the ransomware was not activated on the customer machines.
In a further warning to customers and the media, GMO said it would not distribute the exposed information and would take legal action against anyone who did so. The company also reaffirmed its refusal to pay the attackers.

The overall prevention score can hide what happens after the initial access. If an attacker uses valid credentials, your defenses drop sharply.
The Blue Report 2026 measures defense techniques by technology across 338 million simulations run in customer production environments.
Source: www.bleepingcomputer.com