


Hackers Exploit Critical SonicWall SMA1000 Vulnerability Days After Patch
Attackers are targeting a maximum-severity vulnerability in SonicWall SMA1000 appliances just three days after SonicWall released a patch for the flaw on Tuesday.
Tracked as CVE-2026-102255, the vulnerability affects the Appliance WorkPlace interface on SMA1000 6210, 7210, and 8200v models. It does not affect SSL-VPN running on the SMA 100 series or SonicWall firewalls.
SonicWall SMA1000 flaw enables unauthorized access
According to SonicWall, a remote, unauthenticated attacker could exploit the vulnerability to make the appliance send requests on the attacker’s behalf, access internal functionality, and perform unauthorized operations.
SonicWall did not report active exploitation in Tuesday’s security advisory. However, Previdian founder and security researcher Ryan Dewhurst told BleepingComputer on Friday that the company’s honeypot network had detected an exploitation attempt matching CVE-2026-102255.
“The request targeted the WorkPlace Extraweb interface using a crafted OPTIONS request, reaching the appliance’s internal CouchDB service at 127.0.0.1:5984,” Dewhurst said. “The payload attempted to access the CouchDB design document and call its _rewrite function, while providing an HTTP Basic Authorization header with the credentials admin:admin.”
Dewhurst said the activity is consistent with active exploitation attempts, although Previdian has not yet determined whether any of the attempts successfully compromised systems.
The October vulnerability affects the same WorkPlace interface targeted by previous SSRF vulnerabilities disclosed in July and September 2026. However, CVE-2026-102255 uses a different exploitation technique.
More than 400 SonicWall SMA1000 appliances exposed online
Internet threat-monitoring organization Shadowserver is tracking more than 400 SMA1000 appliances publicly accessible online. There is currently no information about how many are honeypots or how many have been patched against CVE-2026-102255.
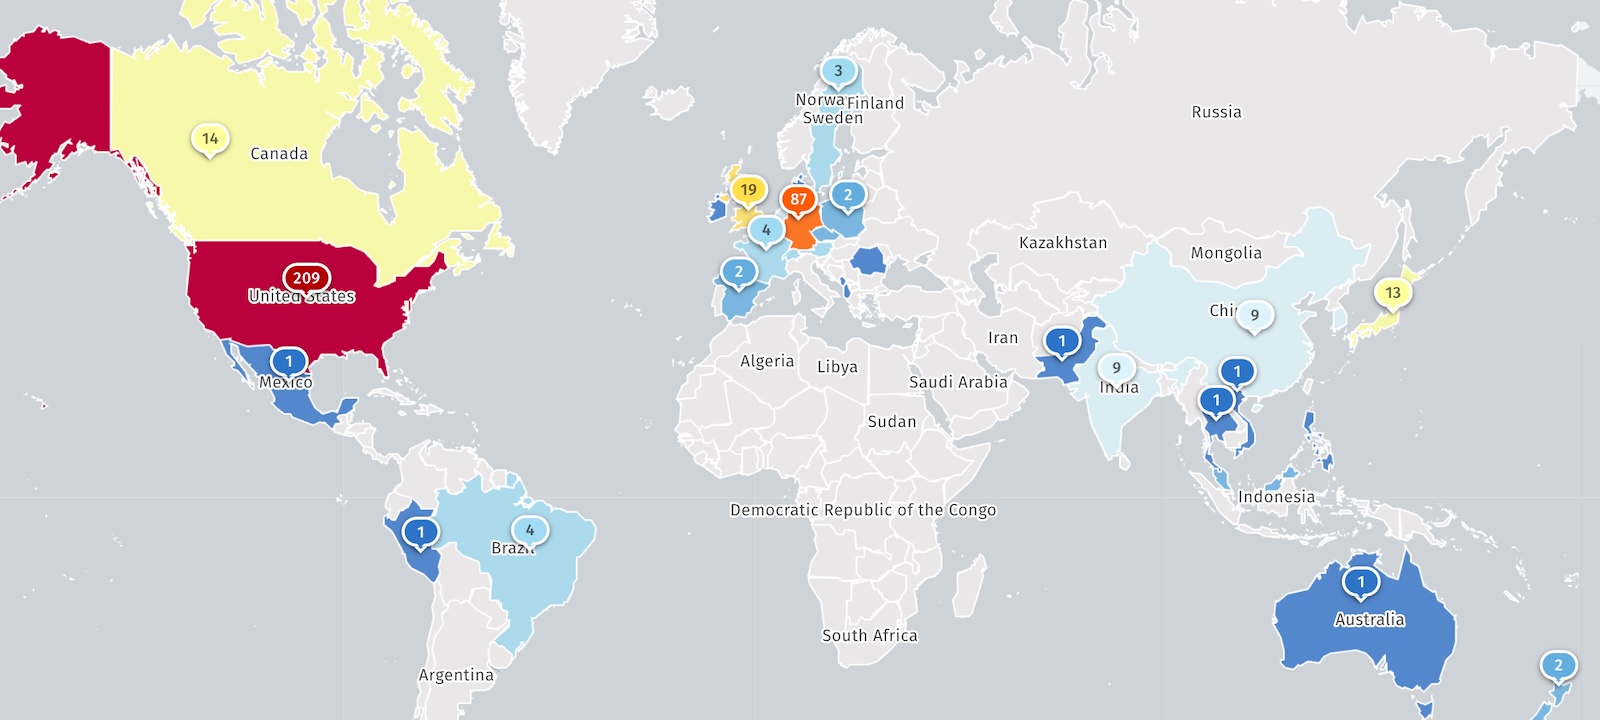
The enterprise-grade SonicWall SMA1000 secure remote access gateway is a frequent target because managed service providers (MSSPs), large enterprises, and government agencies use it to provide VPN access to internal applications and corporate networks.
Previous SonicWall SMA1000 attacks deployed malware
In July, attackers exploited two SMA1000 zero-day vulnerabilities, CVE-2026-15409 and CVE-2026-15410, over several weeks to install the custom Sou5, OrangeTail, and RootRun malware on vulnerable VPN appliances.
The US Cybersecurity and Infrastructure Security Agency (CISA) later linked some of those attacks to ransomware gangs.
Last month, SonicWall also warned customers that attackers were chaining two new zero-day vulnerabilities, CVE-2026-83548 and CVE-2026-83549, to execute remote code on vulnerable SMA1000 gateways.
Over the past four years, CISA has added 19 SonicWall vulnerabilities to its Known Exploited Vulnerabilities catalog. Of those, 13 were flagged as being used by ransomware gangs.
Organizations using affected SonicWall SMA1000 appliances should review SonicWall’s advisory and apply the available security update.

Join Mikko Hypponen and security leaders from the NFL, Chanel, and Atlassian for a 2-hour digital summit about what will change with AI speed attacks, what defenders should stop doing, and how to verify, decide, fix, and revalidate at machine speed.
Source: www.bleepingcomputer.com