


Pwn2Own Ireland 2026 Day One: Samsung Galaxy S26 Hacked Twice as Researchers Exploit 32 Zero-Days
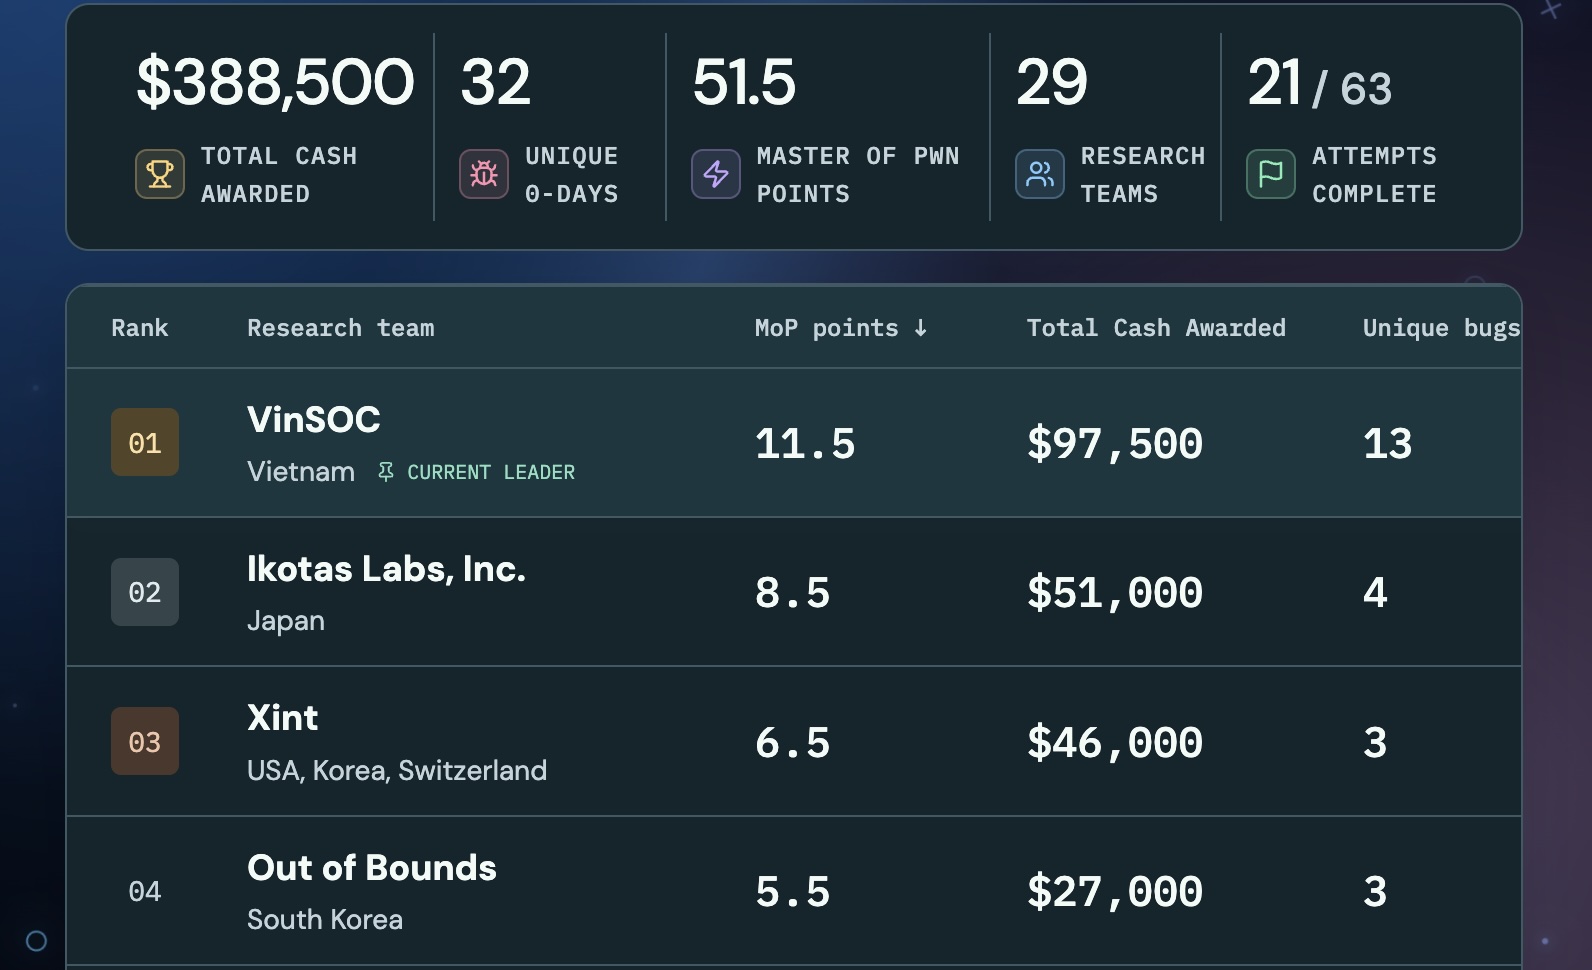
Security researchers exploited 32 zero-day vulnerabilities and won $388,500 on the first day of the Pwn2Own Ireland 2026 hacking competition. The Samsung Galaxy S26 was successfully hacked twice during the event.
Pwn2Own Ireland 2026 targets smartphones, AI and smart home devices
Participants in Pwn2Own Ireland 2026 are targeting products across seven categories, including mobile phones, printers, smart home devices, messaging apps, AI infrastructure, AI coding applications, and wellness and healthcare devices.
The mobile phone category includes the Apple iPhone 17, Samsung Galaxy S26, and Google Pixel 10. The competition’s new categories give researchers additional opportunities to test wellness and healthcare devices.
Samsung Galaxy S26 hacked twice on day one
The day’s highlights included successful Samsung Galaxy S26 exploits by Interrupt Labs, the Ikotas Institute, and Viettel Cyber Security’s Nguyen Thanh Dat.
However, some of the bugs used in the demonstrations were already known to the affected vendors, according to the Zero Day Initiative.
VinSOC leads the Pwn2Own Ireland leaderboard
VinSOC researchers Vũ Chí Thành and Huỳnh Đức Tin currently lead the leaderboard after chaining seven zero-days to win $40,000 by targeting the Philips Hue Bridge Pro smart lighting hub.
The researchers also won an additional $40,000 after using five zero-day exploit chains against Oracle Autonomous AI Database.
Researchers target printers, AI coding tools and smart speakers
Other successful demonstrations on day one included a LiteLLM zero-day, exploits against a Lexmark CX532adwe and Canon imageFORCE 1643F MFP, and an attack that took down the cloud-based OpenAI Codex AI coding agent.
Researchers also exploited a single argument-injection bug and four vulnerabilities to compromise a Sonos Era 300 smart speaker again, as shown in the demonstration.
Mikhail Evdokimov, Polina Smirnova, and Mate Zombor of White Noise Club also targeted the Google Pixel 10, but were unable to get their exploit working within the allotted time.
What happens after a Pwn2Own zero-day is reported?
The Zero Day Initiative (ZDI) organizes Pwn2Own to identify zero-day vulnerabilities in targeted devices before attackers can exploit them in the wild.
After a vulnerability is demonstrated at Pwn2Own, vendors have 90 days to release a security update before Trend Micro’s ZDI publishes details about the vulnerability.
Pwn2Own Ireland 2026 day two and day three targets
On the second day, researchers will again target AI infrastructure, printers, smart home devices, and wellness products. The Samsung Galaxy S26 and Google Pixel 10 will also be targeted in the mobile phone category.
On the third day, researchers will once again attempt to hack the Google Pixel 10 and Samsung Galaxy S26, along with multiple smart home, AI infrastructure, and printer devices.
Pwn2Own Ireland 2025 results
During last year’s Pwn2Own Ireland event, security researchers earned $1,024,750 by demonstrating 73 zero-day vulnerabilities. The Summoning team won $187,500 after hacking a Samsung Galaxy S25, Synology DiskStation DS925+ NAS, Home Assistant Green, Synology ActiveProtect Appliance DP320 NAS drive, Synology CC400W camera, and QNAP TS-453E NAS.

Join Mikko Hypponen and security leaders from the NFL, Chanel, and Atlassian for a two-hour digital summit about how AI-speed attacks will change security, what defenders should stop doing, and how to verify, decide, fix, and revalidate at machine speed.
Source: www.bleepingcomputer.com