


Criminal IP Introduces AITEM to Advance AI-Powered Threat Exposure Management
AI SPERA’s Criminal IP, a cyber threat intelligence platform that provides decision-ready intelligence and attack surface visibility to security teams worldwide, will attend GovWare 2026 in Singapore.
As security operations move beyond asset discovery toward understanding, prioritizing, and responding to exposures, Criminal IP is introducing AITEM—AI-powered Threat Exposure Management—a vision for the next evolution of attack surface management.
Why Attack Surface Management Must Move Beyond Visibility
Traditional attack surface management (ASM) tools help organizations discover Internet-facing assets, including servers, domains, IP addresses, and administrative panels, before attackers find them. However, asset discovery alone is no longer enough.
“Recognizing a threat and responding to it are two completely different challenges,” said Byungtak Kang, CEO of AI SPERA. “Creating a more secure cyber world requires a shift from visibility to action.
“Today’s organizations have more visibility than ever before, but many still struggle to effectively prioritize and act on the risks it uncovers. By applying AI to filter noise, enhance context, and guide investigations, security teams can focus on the most important exposures, respond in real time, and turn insights into meaningful actions.”
As AI lowers the barrier for attackers, the gap between detection and action is becoming more critical. Automated scanning, publicly available proof-of-concept exploit code, and AI-assisted vulnerability detection allow threat actors to identify and target exposed assets faster than ever. For defenders, the challenge is no longer simply achieving visibility—it is responding quickly and effectively.
AITEM Expands Attack Surface Management with AI
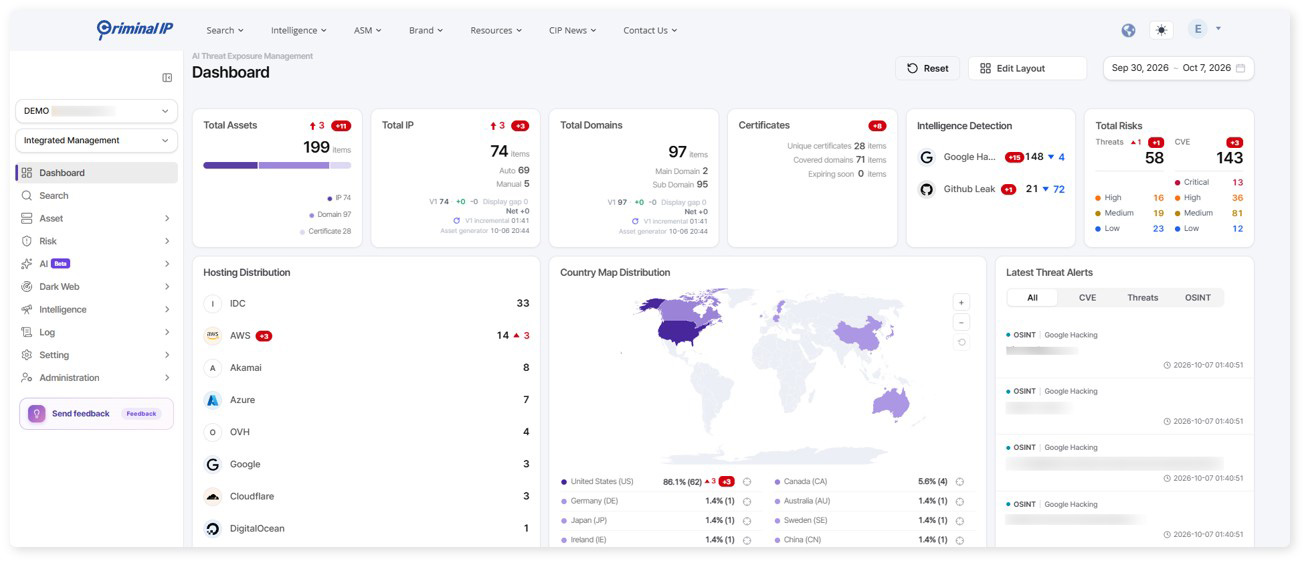
AITEM extends traditional attack surface management beyond external asset inventory. It leverages Criminal IP threat intelligence to incorporate exposures across external assets, open-source intelligence (OSINT), dark web data, internal infrastructure, shadow AI, leaked data, and emerging vulnerabilities as part of a broader threat exposure management approach.
Instead of providing only findings and general risk scores, AITEM is designed to connect fragmented findings with the context security teams need to investigate, prioritize, and respond.
See how AITEM combines Criminal IP threat intelligence and AI to connect exposure discovery, investigation, prioritization, and response.
Gain a broader view of risk across external assets, internal infrastructure, OSINT, dark web data, and shadow AI.
AI Across the Threat Exposure Management Lifecycle
AITEM applies AI across four stages of exposure management:
- Detect – Connect emerging threats and vulnerabilities to the products, services, and assets that exist within an organization’s environment.
- Investigate – Enable security teams to explore assets, exposures, vulnerabilities, and security findings using natural language while bringing relevant context together in one place.
- Prioritize – Assess risk by combining organization-defined criteria with real-world exploitability and attacker activity instead of relying solely on generic vendor risk scores.
- Automate – Convert prioritized findings into alerts, tickets, and workflow actions that can be routed to the appropriate teams, helping move critical exposures from detection to response.
Threat Intelligence at the Core of AITEM
AITEM is built on Criminal IP threat intelligence. It goes beyond vulnerability data by adding real-world context to exposure management.
The platform brings together open ports, exposed services, vulnerabilities, connected infrastructure, exploitation history, scanner activity, threat attributes, and malicious infrastructure. This helps security teams understand not only what is exposed, but also what is happening around that exposure and why it matters.
AITEM represents Criminal IP’s approach to evolving attack surface management. It extends visibility beyond external asset inventory and connects exposure discovery with investigation, threat context, prioritization, and response.
Criminal IP to Present AI-Driven ASM at GovWare 2026
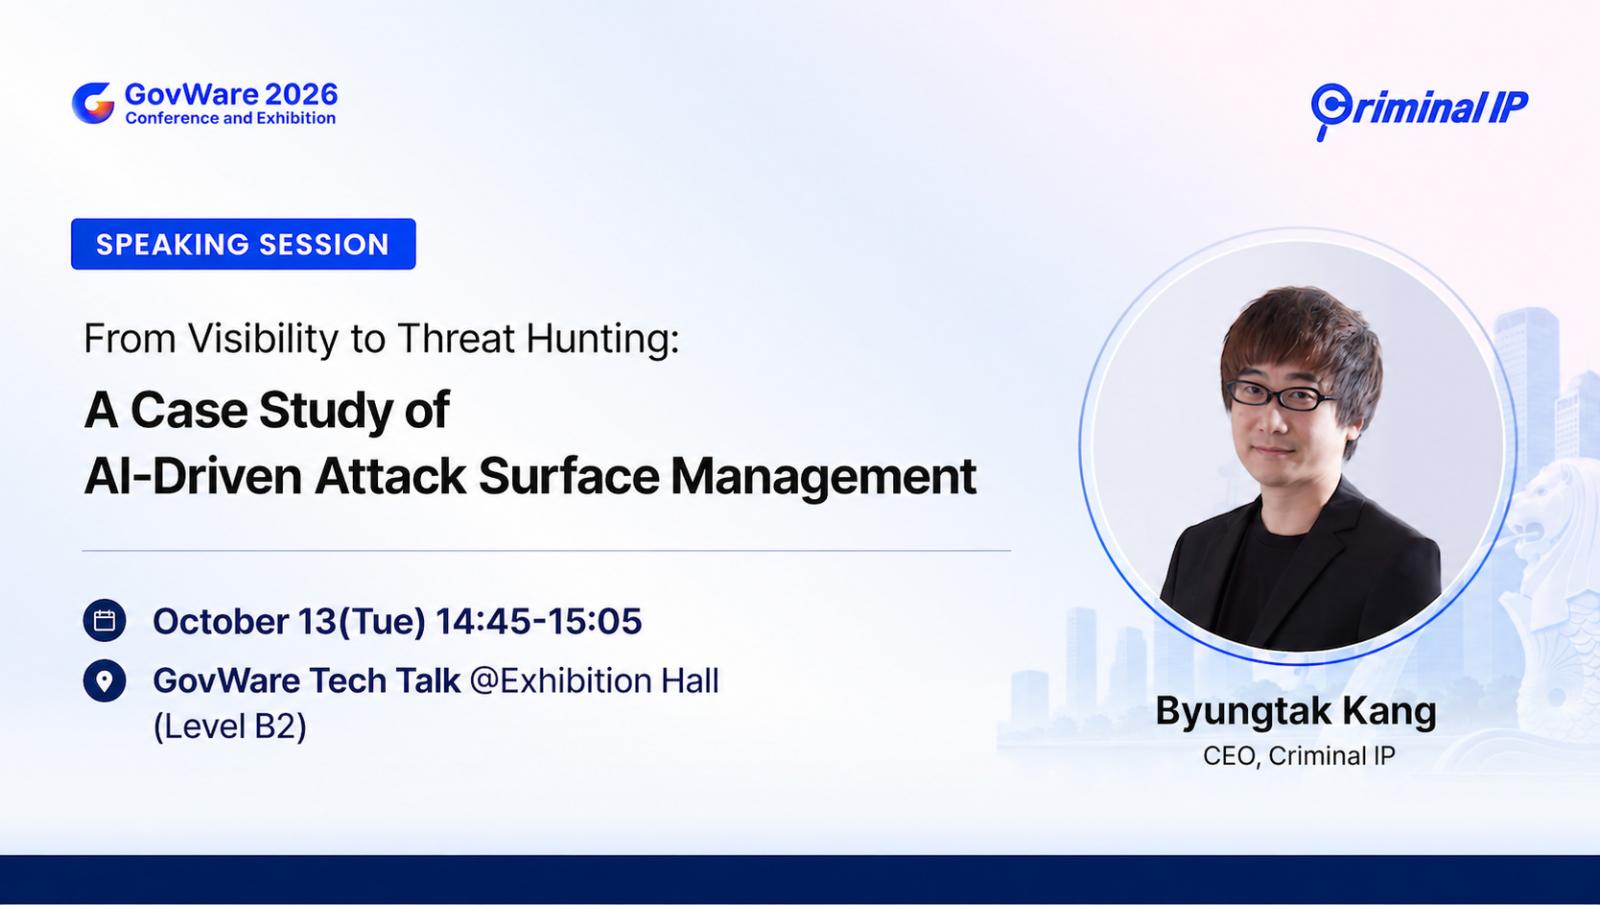
At GovWare 2026, AI SPERA CEO Byungtak Kang will present “From Visibility to Threat Hunting: A Case Study in AI-Driven Attack Surface Management” as part of the conference program.
The session will explore how threat intelligence and attack surface visibility can support faster investigations and more effective security operations. It will use real-world examples to examine the transition from exposure discovery to understanding and response.
How AI Is Changing Security Operations
The direction Criminal IP is pursuing with AITEM reflects broader changes across the global security industry. At RSAC 2026, agent AI, AI SOC, and shadow AI emerged as key themes as leading security vendors continued moving from siloed security tools toward more integrated, AI-driven security operations.
“Competition in ASM is no longer about who can find more assets,” Kang said. “The game will be about who can work faster, respond more effectively, and mobilize the organization. AI should handle the repetitive analytical tasks. Humans should focus on judgment, responsibility, and prioritization.”
About Criminal IP and AI SPERA
Criminal IP is a cyber threat intelligence solution powered by AI SPERA. It provides decision-ready threat intelligence and attack surface management solutions to security teams worldwide.
By continuously scanning the global internet, Criminal IP aggregates and contextualizes threat signals across IPs, domains, URLs, and attack infrastructure. The platform covers malicious indicators, known vulnerabilities, exposed assets, and attacker behavior.
Criminal IP’s mission is to provide real-world visibility into an organization’s cyber environment and accelerate threat detection and response with the intelligence needed to outsmart attackers.
For more information, please visit: www.criminalip.io
Sponsored and written by Criminal IP.
Source: www.bleepingcomputer.com