


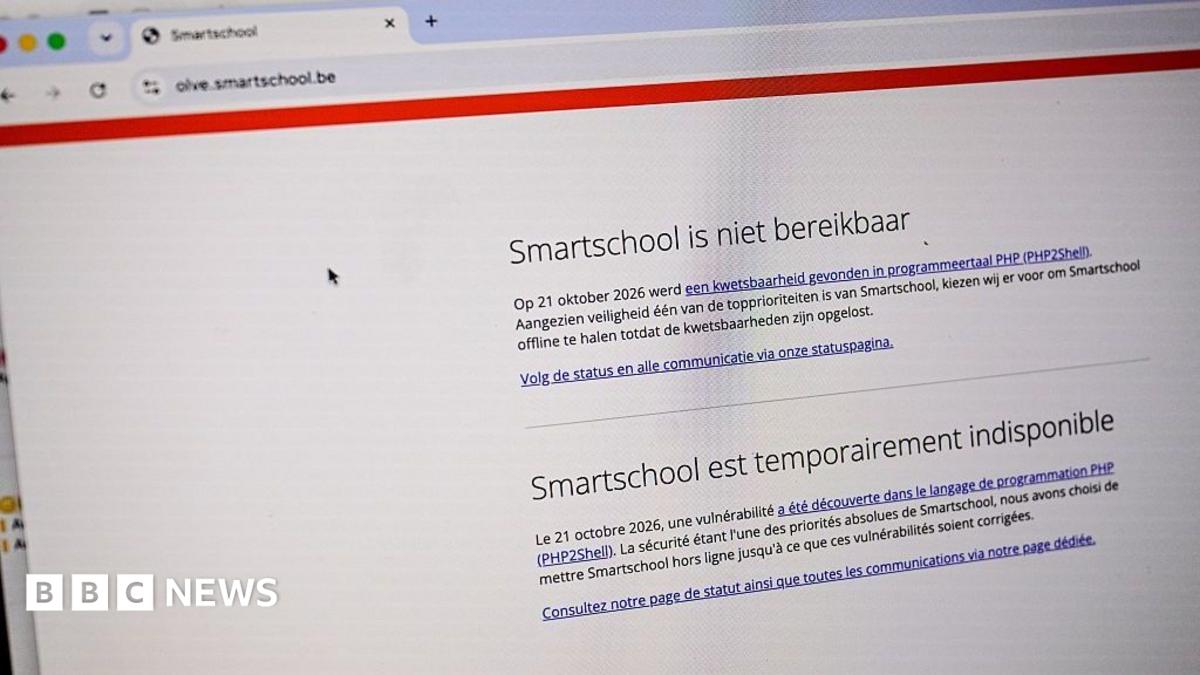
PHP Security Vulnerability Sparks Urgent Patch Rush and Misinformation Concerns
A newly disclosed PHP security vulnerability has prompted developers and IT teams to scramble for a software fix, while cybersecurity experts question rumors that hackers were already exploiting the flaw.
Unsupported PHP Versions Could Require Major Changes
Loganaden Velvindron, an IT administrator from Mauritius, said his team was frustrated after realizing how heavily its software relied on PHP.
“Many versions of PHP that you run are completely unsupported, so you may need to rebuild your web app and make code changes,” he said.
He said one challenge was that announcements about PHP security vulnerabilities sometimes appeared without enough warning, leaving organizations little time to prepare and respond.
PHP Patch Triggers a Race to Update
The warning also prompted Jon Jones, a technical director at a digital advertising company, to take action.
“Seeing the warning go down was definitely an eye-opener and a new experience that I had never dealt with before,” he said.
“But in a way, it felt exciting, like a Hollywood action scene.”
The PHP Foundation, which maintains the programming language, released a software fix, triggering a rush to download and install it.
Mr Jones said it felt like “the race was on” when the patch was released at 15:00 BST on Wednesday.
“As anyone who has ever applied a software update knows, there’s always the possibility that an update could introduce other issues, so I was a little nervous,” he said.
Experts Question Rumors of Active PHP Exploitation
The uproar began after someone leaked early details about a flaw in PHP. Rumors quickly spread that cybercriminals were already attempting to exploit it.
Cybersecurity experts are now questioning whether those reports are accurate.
“We’ve received a lot of crappy information about hackers actively using proof-of-concept techniques,” said British cyber expert Daniel Card.
He said he had felt sick since Tuesday, when rumors of the PHP hack began spreading.
“This isn’t the first time a situation like this has happened, but it feels like it’s on another level,” he said.
Although he agreed that the PHP vulnerability was very serious and should be treated that way, he and others were frustrated by misinformation suggesting that hackers were already on the loose.
Source: www.bbc.co.uk