


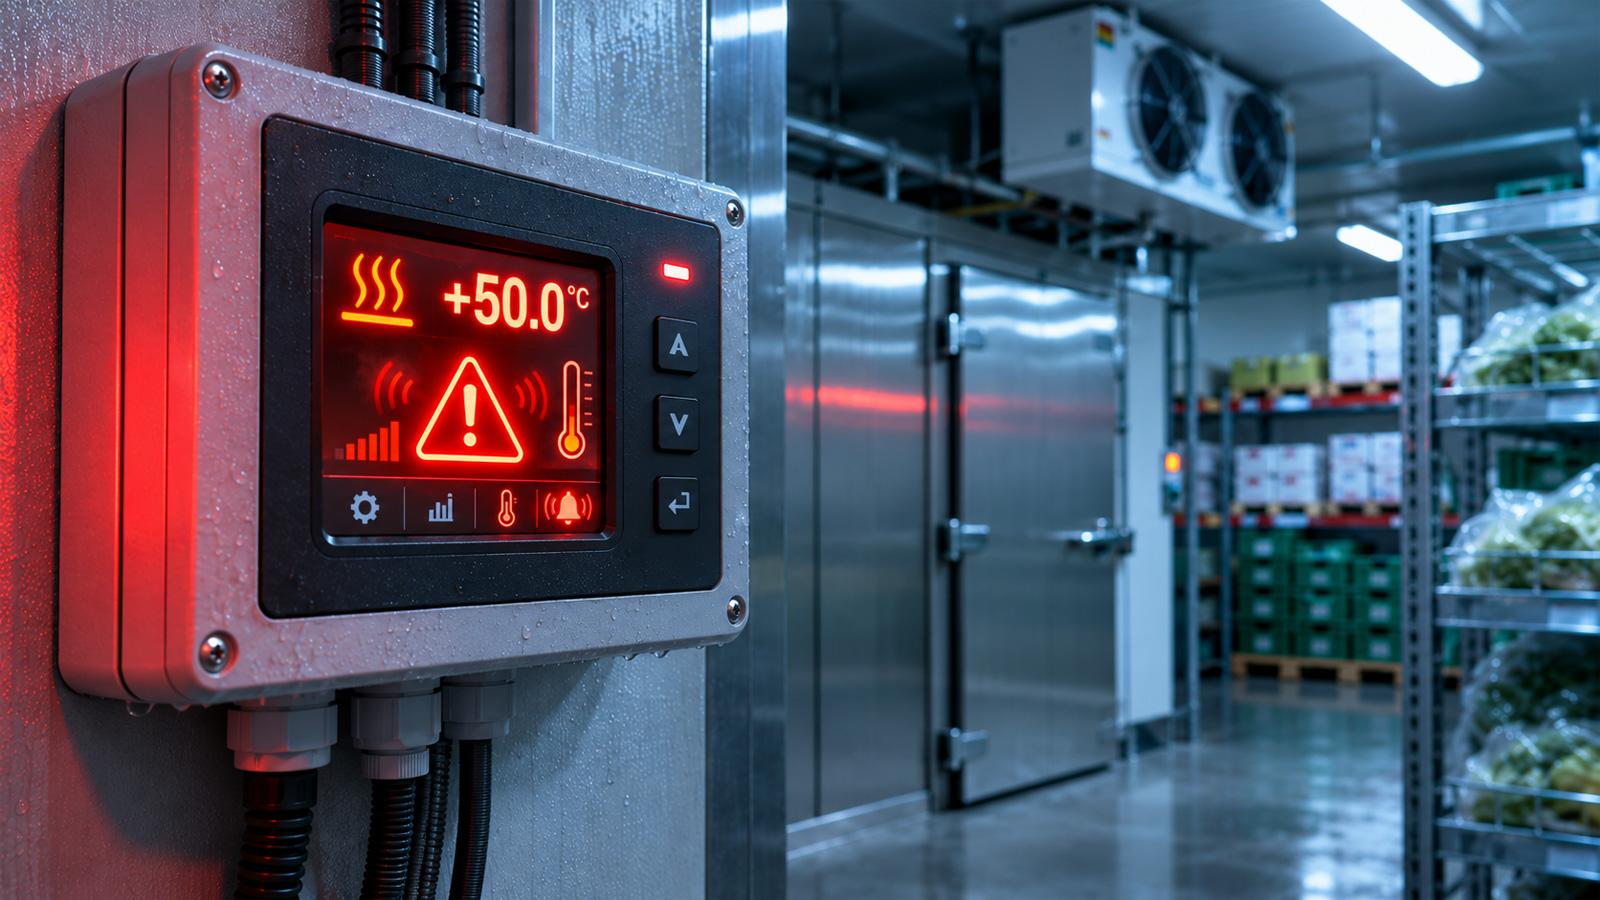
The FBI and CISA warn that hackers are actively targeting industrial refrigeration and cold-chain monitoring systems worldwide. Successful attacks could spoil food and medical supplies, damage equipment, create fire hazards, and prevent operators from seeing dangerous temperature changes.
The warning was issued jointly with the U.S. Department of Health and Human Services (HHS), the Department of Agriculture (USDA), and the Department of Transportation (DOT). The agencies urged critical-infrastructure operators to secure refrigeration control equipment used in healthcare, food production, chemical facilities, and transportation.
“All organizations that rely on refrigeration and surveillance systems should expect that their refrigeration systems may become targets,” said Chris Butera, CISA acting deputy director for cybersecurity.
Hackers target exposed refrigeration controllers
According to the joint recommendation, attackers are exploiting weaknesses in unpatched electronic temperature controllers and commercial refrigeration management systems that are accessible from the internet.
These devices allow operators to remotely monitor temperatures, manage defrost cycles, and control cooling equipment.
“Globally, malicious cyber attackers are targeting vulnerabilities and weaknesses in unpatched or internet-accessible electronic temperature controllers and commercial refrigeration controllers in retail grocery stores and refrigeration facilities,” CISA warned.
The agencies said attackers could exploit authentication-bypass vulnerabilities, arbitrary-code-injection flaws, or insecure configurations to change temperature settings. They could also force refrigeration equipment to run continuous heating or defrost cycles.
A successful attack could cause inventory loss, shorten equipment life, create fire hazards, and produce unsafe storage conditions. Attackers could also reduce visibility into current temperatures, preventing operators from detecting a developing problem.
European attacks disrupted refrigeration systems
The warning follows a series of attacks on refrigeration systems in Europe that disrupted supermarkets and blood-storage facilities.
In October, hackers compromised the refrigeration controllers of an estimated 250 to 350 supermarkets in France. The attackers remotely activated defrost functions, increasing the temperature of refrigerators and freezers.
A second wave of attacks reported in November affected more than 115 stores in six European countries. Some refrigeration systems shut down completely, while temperatures in others rose to 50 degrees Celsius (122 degrees Fahrenheit).
On November 3, the French Blood Service (EFS) confirmed that a cybersecurity incident involving a refrigeration-equipment provider had changed temperature and defrost settings at three facilities storing blood products.
Agencies recommend isolating refrigeration systems
In response to the ongoing threat, U.S. government agencies are asking organizations to remove refrigeration control equipment from the public internet while preserving only the remote access they need. They also recommend changing default passwords and applying available security updates.
The guidance further recommends separating operational technology systems from business networks and configuring safe thermal limits so controllers cannot operate outside acceptable temperature ranges.
Source: www.bleepingcomputer.com