


Microsoft Entra ID to Block External Scripts During Sign-Ins in October 2026
Microsoft has notified customers that Microsoft Entra ID will soon enforce additional protections against external script injection attacks during browser-based sign-ins.
Beginning in mid-October 2026, Microsoft will apply Content Security Policy (CSP) defenses that allow only scripts hosted on trusted Microsoft Content Delivery Network (CDN) domains to run during Entra ID authentication. The rollout is expected to be completed by late October 2026.
Microsoft Entra ID adds CSP protection against XSS attacks
Microsoft first announced plans to protect Entra ID sign-ins from script injection attacks in November 2025. The new controls are designed to block unauthorized or externally injected code, helping protect users from cross-site scripting (XSS) and other sign-in security risks.
In a Monday Message Center update seen by BleepingComputer, Microsoft said:
“Microsoft Entra ID will strengthen sign-in security by enforcing content security policies that block external script injection starting in mid-October 2026. This change helps protect users from threats such as cross-site scripting (XSS) by allowing only trusted scripts hosted by Microsoft to run during authentication and blocking unauthorized or externally injected code.”
Once the rollout is complete, the protections will apply automatically to users signing in through the browser-based Entra ID experience.
Browser extensions and script injection tools may stop working
Microsoft advised business customers to stop using browser extensions and other tools that inject code or scripts into Entra ID sign-in pages before the CSP changes take effect.
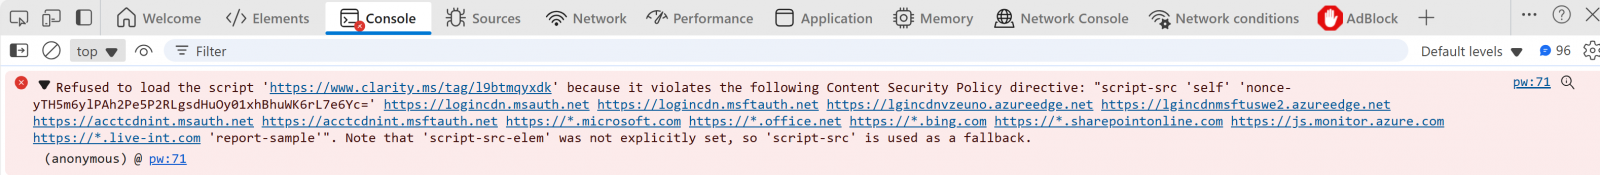
Organizations should use the remaining time to test their sign-in scenarios and identify potential compatibility or dependency issues. Administrators can review the sign-in flow in a browser’s developer console and look for CSP violations, which appear as red messages containing details about blocked scripts.
Microsoft said users will still be able to sign in if an unsupported script injection tool stops working. The change will be enabled by default as part of a service update and will not require tenant configuration.
MSAL and API authentication flows are not affected
The new CSP enforcement applies only to the browser-based sign-in experience using login.microsoftonline.com. Microsoft Authentication Library (MSAL) and API-based authentication flows will not be affected.
Administrators should therefore focus testing on browser-based Entra ID authentication and any extensions, custom tools, or other software that modifies those sign-in pages.
Entra ID changes are part of Microsoft’s Secure Future Initiative
The changes are part of Microsoft’s Secure Future Initiative (SFI), which was announced after Chinese hackers breached the Exchange Online mailboxes of dozens of organizations and hundreds of individuals worldwide in May and June 2023.
As part of the same effort, Microsoft has updated Microsoft 365 security defaults to disable all ActiveX controls in Windows versions of Microsoft 365 and Office 2024 apps. The company has also blocked access to Office, SharePoint, and OneDrive files through traditional authentication protocols.
Microsoft’s Message Center announcement includes additional details about the Entra ID CSP enforcement.

Join Mikko Hypponen and security leaders from the NFL, Chanel, and Atlassian for a 2-hour digital summit about what will change with AI speed attacks, what defenders should stop doing, and how to verify, decide, correct, and revalidate at machine speed.
Source: www.bleepingcomputer.com