


Zeabur Breach Exposes 3.2 Million Environment Variables and 321,810 Accounts
Development platform Zeabur has disclosed a major cybersecurity incident in which attackers used leaked internal credentials stored in cleartext to compromise its infrastructure and steal more than 3.2 million environment variable records and information associated with 321,810 accounts.
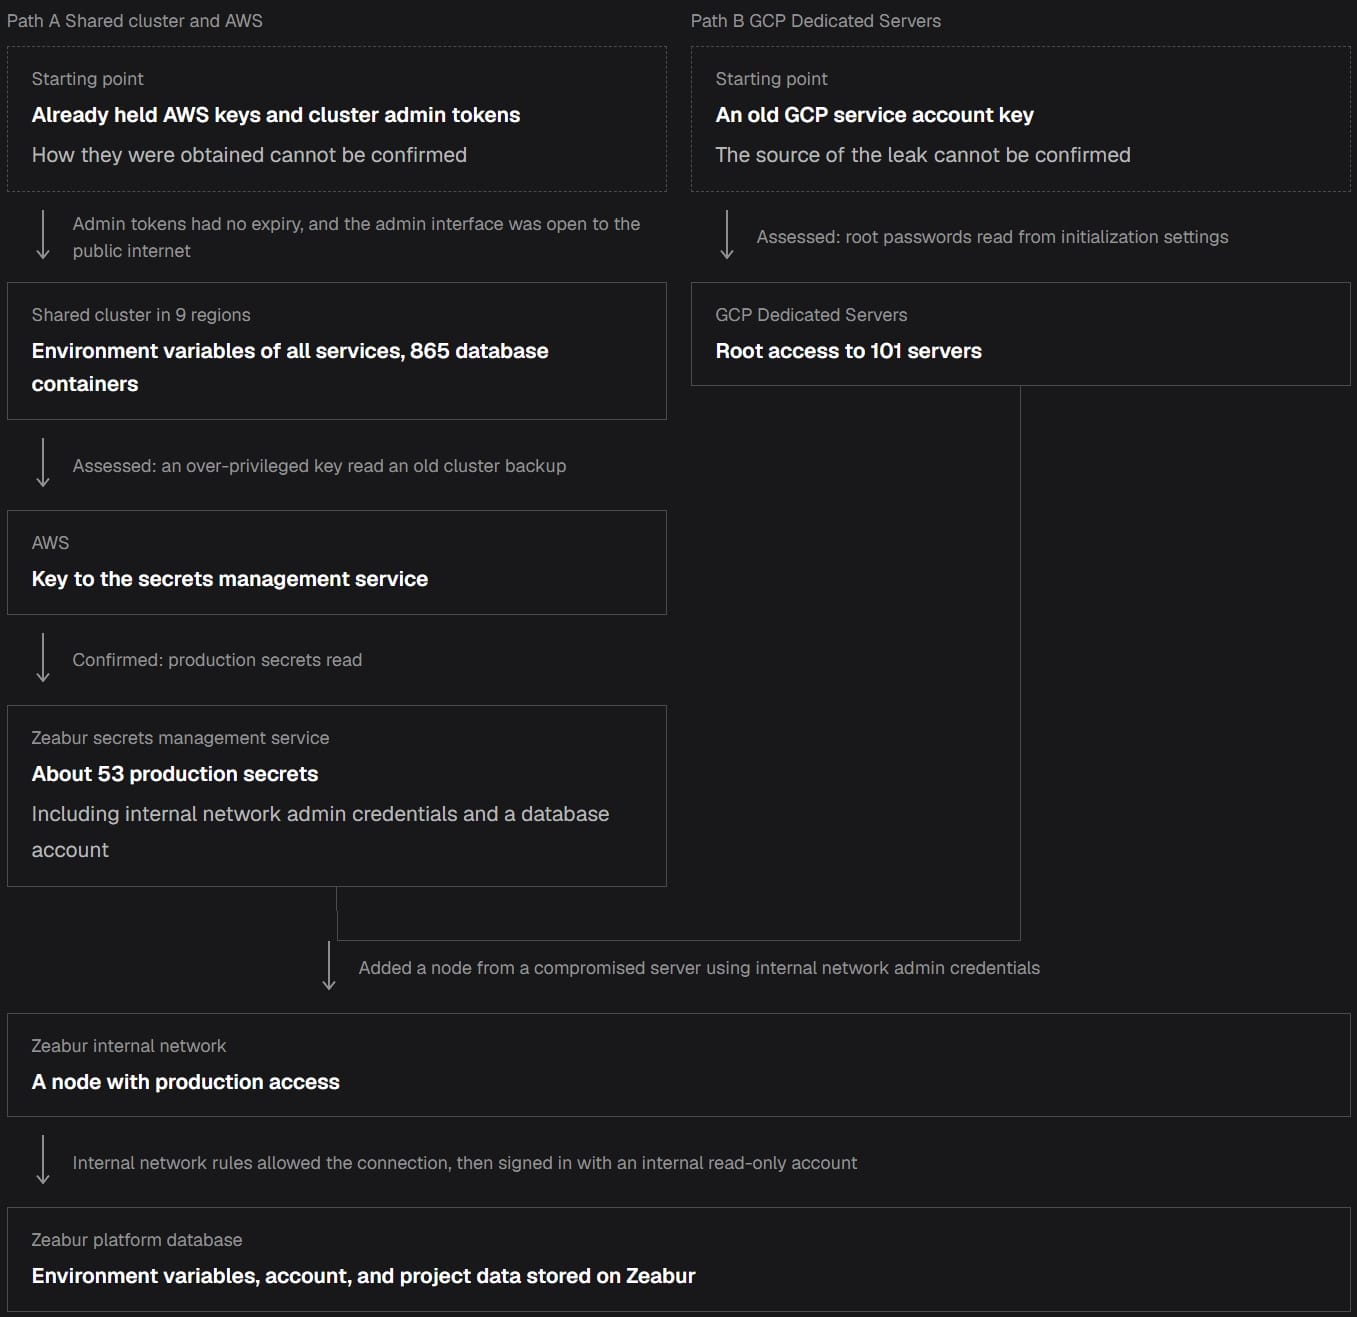
The attackers used stolen administrator credentials and cloud access keys to compromise Zeabur’s shared hosting infrastructure and dedicated servers before gaining access to the company’s operational database.
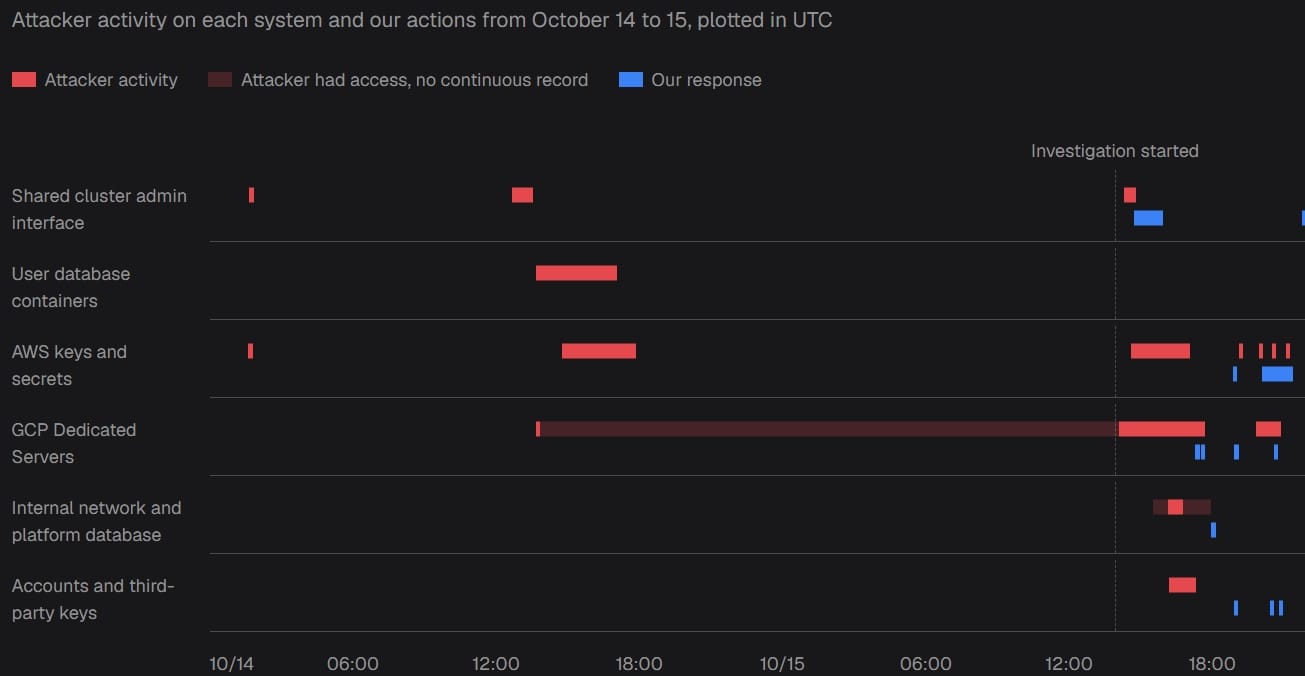
“Between October 14 and 15, 2026, attackers used compromised Zeabur internal credentials to compromise shared clusters, some dedicated servers, Zeabur’s internal systems, and ultimately read the platform database,” Zeabur said in its announcement.
Source: Zeabur
How attackers compromised Zeabur
Zeabur is a developer hosting and deployment platform that lets users connect GitHub repositories while the platform manages deployment, databases, HTTPS, and infrastructure.
In late August 2026, the company suffered another security breach when a hacker exploited a flaw in a customer’s NextChat application and moved through poorly isolated internal systems.
That earlier incident resulted in the theft of AWS credentials and access to Zeabur’s production database, exposing account information, API keys, and other sensitive data stored there.
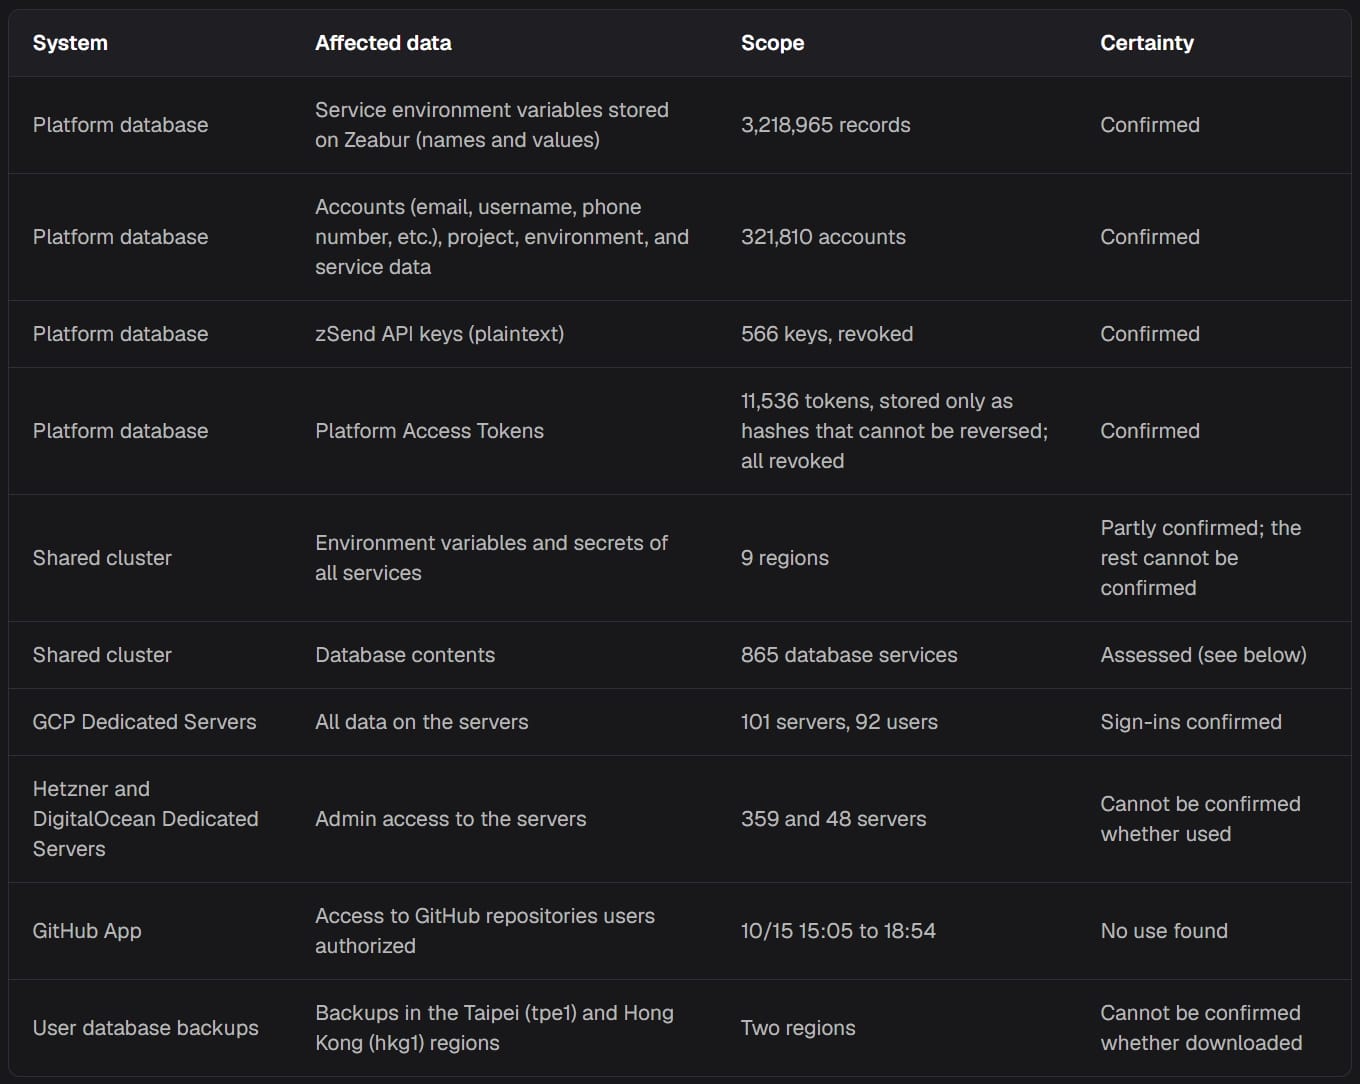
Zeabur said the latest breach was more extensive. It affected a shared cluster spanning nine regions, 321,810 accounts, and approximately 3.2 million environment variable records.
The company also observed root sign-ins by 92 users to 101 Google Cloud Platform servers. Attackers added SSH keys to 50 servers and attached 16 customer disk copies to their own virtual machines.
Source: Zeabur
Leaked credentials were not rotated after August breach
Zeabur said the attackers likely obtained the credentials used in the latest attack during the August breach, although the company has not confirmed the connection.
The company acknowledged that it failed to encrypt credentials before storing them and did not rotate credentials for all administrator accounts after the August incident. The administrator portal also remained accessible from the public internet.
“The admin token does not have an expiration date, has not been rotated since it was created in January 2024, and has not been included in the rotation since August,” Zeabur explained.
Zeabur is urging users to immediately rotate exposed credentials and secrets, revoke active sessions, and rebuild compromised GCP servers.
Environment variables that had previously been migrated to customers’ own servers as part of the response to the August incident were not included in this platform database leak. However, those variables could still be exposed if a customer’s host was compromised.
Source: Zeabur
Zeabur will shut down by the end of 2026
Following the latest security incident, Zeabur announced over the weekend that it will suspend services beginning December 1, 2026, and end its service by December 31, 2026.
The decision follows three and a half years of continued growth, including a record year in 2026. However, Zeabur said that scaling its projects to meet market demand had made the platform increasingly complex and difficult to maintain, and that its recent security failures reflected those challenges.
“After the August incident, we spent a long time discussing and struggling with what to do next,” Zeabur explained.
“Following this latest incident, we re-evaluated what we need to do to continue operating and the responsibilities that our team can fulfill. Ultimately, we have decided to scale back our operations.”
On December 1, updates will be disabled and all services running on shared clusters will be paused. By the end of the year, dedicated servers will expire and be shut down, while all shared clusters will stop operating.
Users may receive additional time to migrate their data, but Zeabur has not yet provided a specific timeline.

The overall prevention score can hide what happens after the initial access. If an attacker uses valid credentials, your defenses drop sharply.
The Blue Report 2026 measures defense techniques by technology across 338 million simulations run in customer production environments.
Source: www.bleepingcomputer.com