


Third-Party.com Used in ClickFix Attack to Target Windows Users With Fake Cloudflare CAPTCHA
The third-party.com domain, commonly used as a placeholder in developer documentation and code examples, has been used to host a fake Cloudflare validation page designed to trick Windows users into running malicious PowerShell commands.
Developers have long used third-party.com to represent an external website, API, or service, much like example.com. However, unlike example.com, example.net, and example.org—which are reserved by IANA for documentation—third-party.com is a registered domain whose owner can control its content.
That difference has become a security concern after attackers used the domain in a ClickFix attack that spoofed Cloudflare security checks.
Fake Cloudflare CAPTCHA copies a PowerShell command
Manifold Security first reported the malicious use of third-party.com while investigating public AI skills and MCP server documentation that referenced the domain.
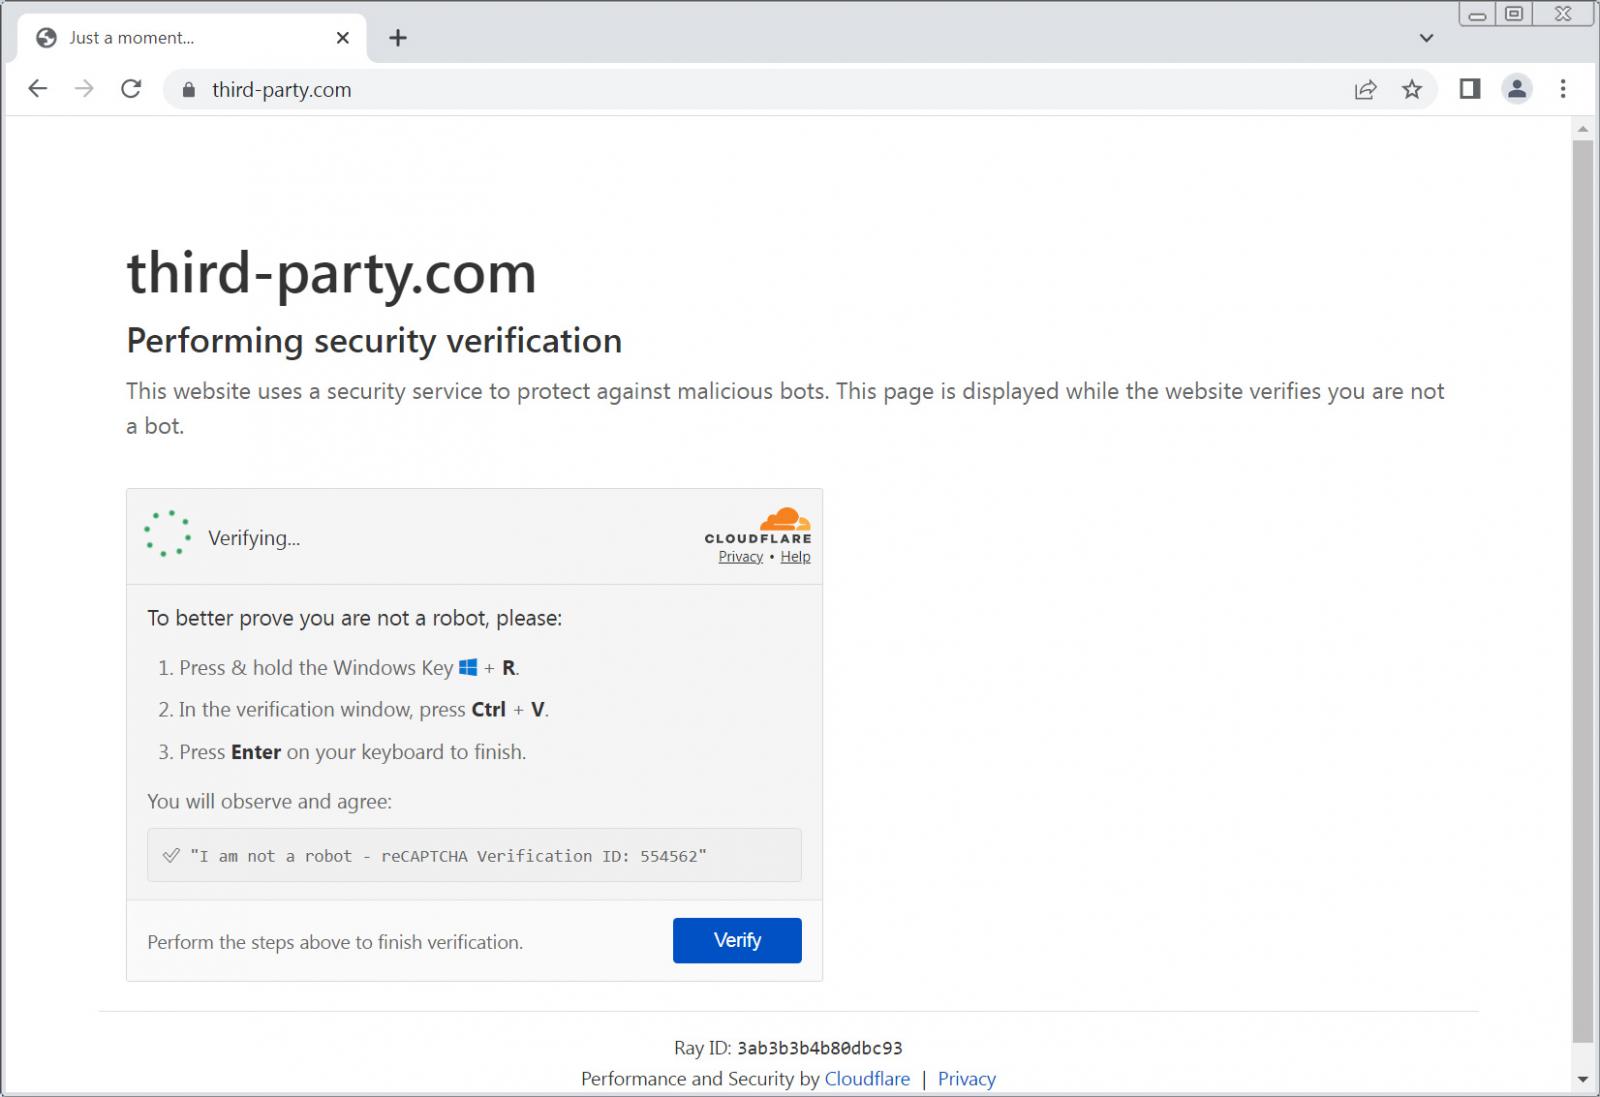
BleepingComputer subsequently observed that the website displayed a fake Cloudflare “Perform Security Verification” CAPTCHA page asking visitors to verify that they are human.
When a user clicks the confirmation box, the page copies a malicious PowerShell command to the Windows Clipboard. The visitor is then instructed to press Windows Key + R, paste the command with Ctrl + V, and press Enter.
Source: BleepingComputer
After the PowerShell command runs, it rebuilds the payload URL and downloads a PowerShell script from:
elxxvvx[.]xyz/fClickFix attacks use fake errors, CAPTCHA prompts, or security checks to persuade victims to manually run commands copied to their clipboard.
The technique has become a common malware distribution method because the victim, rather than a website or email attachment, initiates the installation by running the command. In some cases, this can help malware bypass traditional antivirus protections.
Attack chain targeted Windows users
At the time of BleepingComputer’s testing, elxxvvx[.]xyz no longer resolved, leaving the current attack chain broken.
However, a Hybrid Analysis report indicated that, as of May 2, 2026, the site was distributing a PowerShell script configured to download a 134 MB ZIP archive from:
https://elxxvvx[.]xyz/update2.zipThe script attempted to save the archive as update26.zip, extract its contents, and launch an executable named draw.io.exe.
The update2.zip archive is no longer available, so BleepingComputer could not determine what the payload was designed to do.
According to Manifold’s Ax Sharma, the attack specifically targeted Windows users. Visitors using Linux or macOS saw an error stating that their operating system was not supported.
“A macOS or Linux user agent will pick up nothing of the sort. You’ll see almost the same page, but it will stop with the following error: ‘macOS is not supported.’ You need a Windows PC to access this website. There is no clipboard poisoning, no payload,” Sharma explained.
“An attacker only reveals a weapon to the target it interacts with, which is why a casual look or scanner on a Linux data center IP will tell you there is nothing wrong with it.”
Why attackers chose third-party.com
The most notable aspect of the campaign is the choice of third-party.com as the host for the ClickFix page.
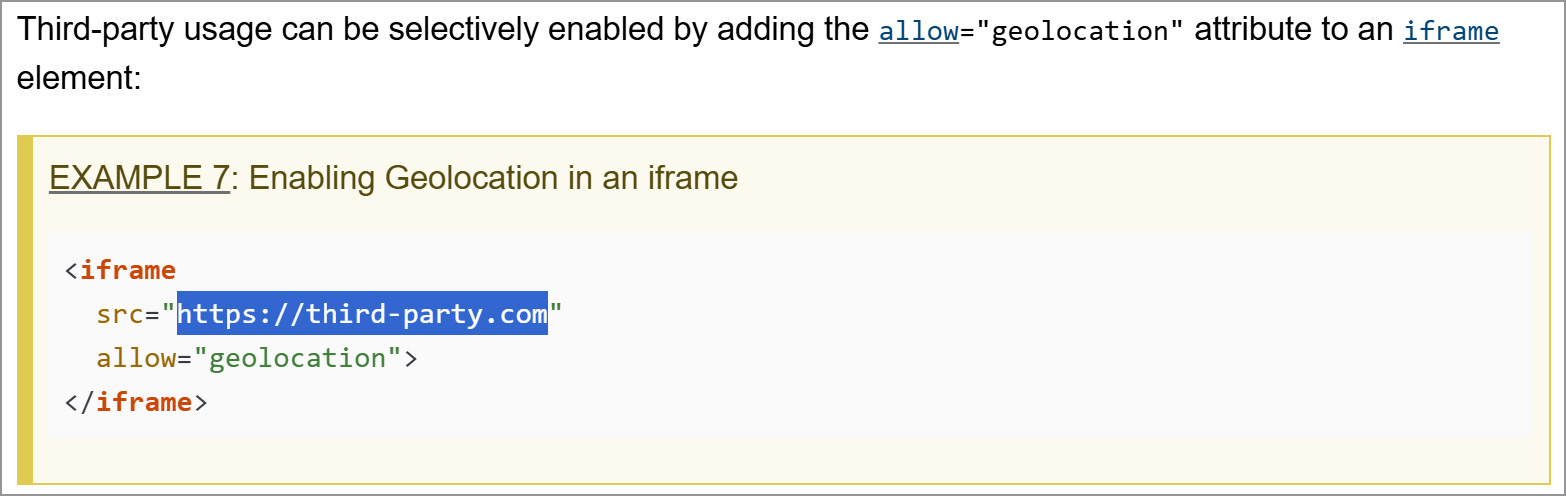
Public developer documentation has used the domain for years as an example hostname. For example, the W3C Geolocation Specification uses third-party.com when demonstrating how to grant geolocation permissions to an external iframe.
The W3C Compute Pressure Specification also uses the domain when demonstrating how to enable remote content APIs on a website:
<iframe src="https://third-party.com" allow="compute-pressure"></iframe>Chromium’s Telemetry extension API documentation similarly uses third-party.com as an example website that can communicate with a Chrome extension.
Some examples go further by placing the domain directly in code that would make a network request if copied without modification. A Privacy CG proposal, for instance, uses the domain as the destination for JavaScript fetch() requests from a service worker.
Online posts also indicate that developers have copied similar examples directly into their own code and projects. In a 2015 Stack Overflow question, a developer said they had applied an asynchronous-loading sample to a website before discovering that it did not work as expected after publication.
Placeholder domains can become security risks
These examples do not indicate that the related projects or documentation were compromised.
However, applications or test code that copies placeholder URLs without replacing them could cause browsers or automated tools to access the live third-party.com domain. That could expose users to ClickFix prompts or other malicious content.
Unlike example.com, which IANA maintains specifically for documentation and does not allow to be registered or transferred, third-party.com has no comparable protection. The domain was clearly registered or taken over at some point and used to deliver the ClickFix attack.
“third party[.]com has been a generic document placeholder for many years, serving the same role as example.com,” Manifold said.
“Searching public code, we found more than 1,500 files across skills, MCP server documentation, and more than 1,700 repositories from trusted names like Chromium, Sanity, and Vercel, all under the lure of ClickFix since at least June 2026.”
The widespread use of third-party.com in documentation makes it attractive to attackers, although there is no evidence that the domain was registered specifically for malicious purposes.
The domain was first registered in 1996, long before the current campaign. BleepingComputer has not determined when or how control of the website changed.
There are currently no reports that references to third-party.com caused ClickFix attacks to execute on developer devices or inside applications and webpages.
Nevertheless, the domain remains live and could be redirected to a new payload domain or used in future attacks.

Join Mikko Hypponen and security leaders from the NFL, Chanel, and Atlassian for a two-hour digital summit about AI-speed attacks, what defenders should stop doing, and how to verify, decide, fix, and revalidate at machine speed.
Source: www.bleepingcomputer.com