


ClosedQuorum Windows Malware Uses AI Models to Autonomously Choose Attack Actions
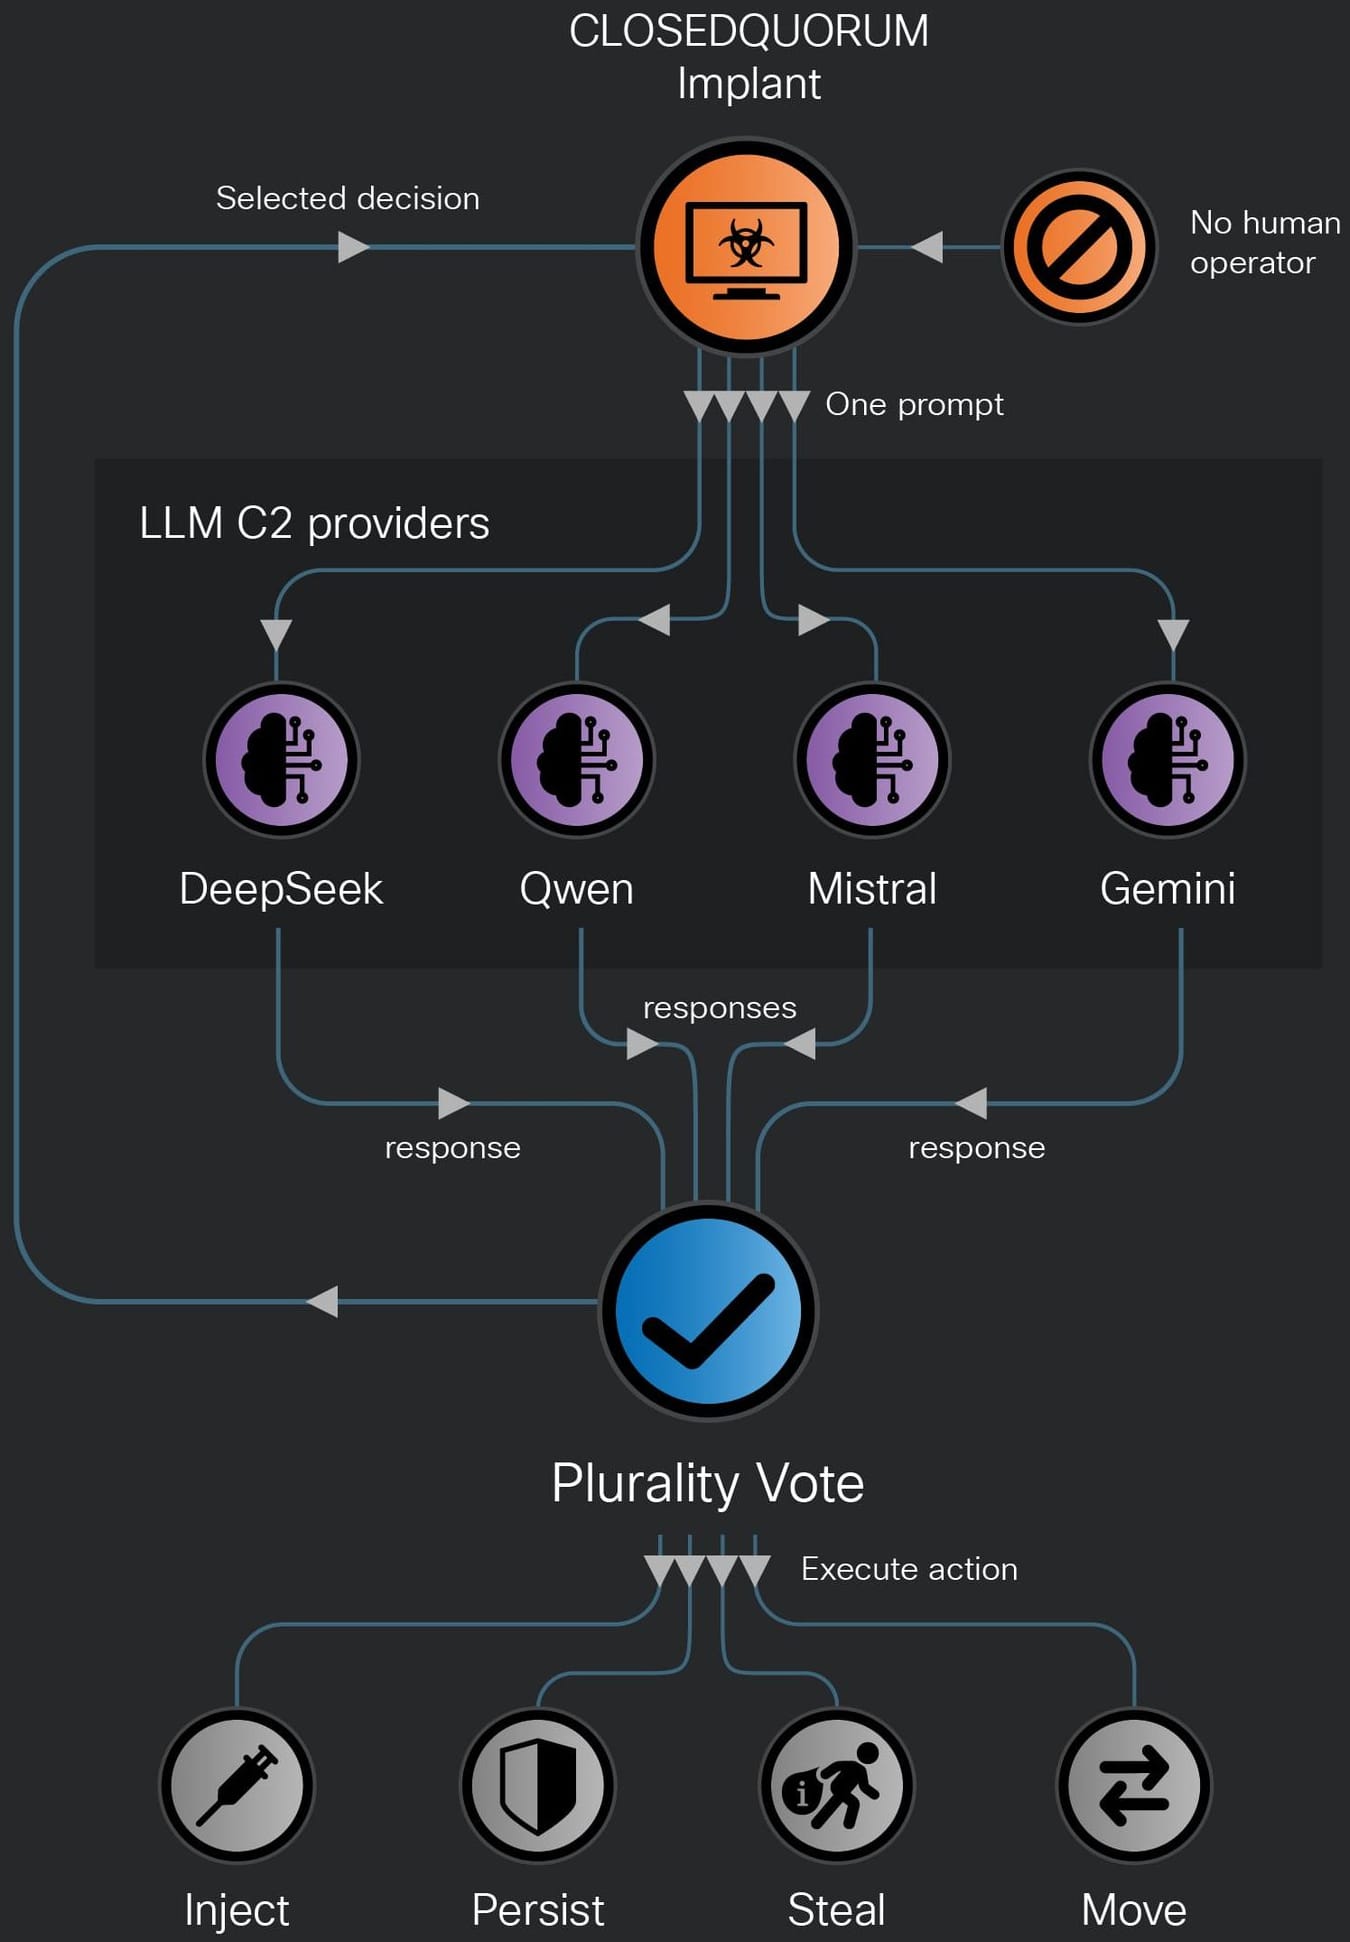
A new Windows malware strain called ClosedQuorum uses Google Gemini, DeepSeek, Qwen, and Mistral AI models to autonomously decide what actions to take after compromising a system.
The Go-based malware operates without commands from a human operator. Instead, it uses reconnaissance data and a voting system to determine its next steps against infected hosts.
If the AI models reach a tie, DeepSeek makes the final decision based on the option it considers most appropriate. Qwen, Mistral, and Gemini are used afterward in that priority order.
What actions can ClosedQuorum perform?
Cisco Talos researchers analyzing ClosedQuorum say the malware is limited to a predefined set of possible decisions:
- Theft: Simultaneously dumps LSASS credentials, steals credentials from Chrome, Edge, and Firefox, and extracts cryptocurrency wallet data from MetaMask, Exodus, and Ethereum-related wallets.
- Inject: Generates shellcode and uses process hollowing or Early Bird APC injection.
- Last: Runs the malware’s persistence module.
- Move: Determines whether lateral movement may be possible. However, the analyzed distribution build does not include a corresponding handler, so this action cannot be performed.
Stolen information is sent to the operator through a Discord webhook, allowing the attack to operate autonomously once the malware has been delivered.
Source: Cisco
AI models make malware decisions without human operators
Talos describes ClosedQuorum as the first publicly documented Windows implant to delegate tactical command-and-control (C2) decisions to a panel of AI models.
According to the researchers, this design could increase the speed and scalability of malicious operations. It also removes the need for continuous human intervention, allowing the attack chain to proceed at any time.
However, the system also introduces potential points of failure. ClosedQuorum may be affected when AI service rate limits are reached, model output is malformed, or the commercial APIs it depends on become temporarily unavailable.
ClosedQuorum may be a test rather than active malware
Cisco Talos says ClosedQuorum is not sophisticated malware, making it unclear whether the sample represents a real-world threat, a test, or an experiment. Nevertheless, the researchers warn that it signals an “architectural shift towards automation of the attack chain.”
“Although we have no confirmation of field deployment, binary artifacts were used to link developers to criminal forum posts related to carding as far back as 2025.” Learn more from Cisco Talos.
The binaries analyzed by Cisco Talos contain placeholder API credentials and a dummy Discord webhook. Authors could add their own credentials and webhook to customized ClosedQuorum builds.
How Cisco Talos discovered ClosedQuorum
Cisco Talos discovered ClosedQuorum using Cairn, an open-source toolkit designed to help researchers track and analyze AI-integrated malware.

Join Mikko Hypponen and security leaders from the NFL, Chanel, and Atlassian for a 2-hour digital summit about what will change with AI-speed attacks, what defenders should stop doing, and how to verify, decide, fix, and revalidate at machine speed.
Source: www.bleepingcomputer.com